








Cybersecurity in IoT: How Businesses Can Secure Connected Devices and Networks
 Share -


- 01Why Cybersecurity Has Become Critical for Enterprise IoT
- 02How IoT Cybersecurity Differs From Traditional IT Security
- 03Types of IoT Cybersecurity Threats Businesses Must Prepare For
- 04Cybersecurity Challenges in Using IOT Across Major Industries
- 05IoT Security Solutions for Industry-Specific Risks
- 06IoT Security Best Practices Across the Device Lifecycle
- 07Cost of Cybersecurity in IoT: Investment Versus the Cost of Inaction
- 08IoT Cybersecurity Use Cases Across Business Environments
- 09IoT Security Standards and Regulatory Requirements Businesses Must Consider
- 10Emerging Trends Shaping the Future of IoT Security
- 11How AI Is Changing IoT Cybersecurity
- 12How Appinventiv Helps Businesses Build AI-Ready IoT Security
- 13FAQs
Key takeaways:
- Every connected device adds a potential entry point across the wider enterprise environment.
- IoT attacks can disrupt equipment, operations, customer services, data, and physical safety.
- Strong protection must cover devices, firmware, networks, APIs, applications, and cloud platforms.
- Security should follow the device from vendor assessment through deployment, maintenance, and retirement.
- AI can uncover unusual behaviour and reduce alert overload, but critical responses still need human oversight.
- Businesses need an experienced security partner that understands their industry, operational limits, and compliance duties.
Every connected device added to your business can improve visibility, automation, and operational control. It can also create another entry point into your enterprise network. A compromised sensor, camera, medical device, fleet tracker, or industrial controller may expose systems far beyond the affected device.
For business leaders, this is not simply an IT concern. An IoT attack can halt production, interrupt customer services, expose regulated information, damage equipment, and create significant compliance liabilities. The impact can quickly spread across operations, finance, customer experience, and brand reputation.
The risk increases when your connected-device estate grows faster than your security controls. Teams may lose track of deployed assets. Vendors may stop providing firmware updates. Default credentials can remain active. Sensitive data may also pass between devices, applications, and cloud platforms without sufficient protection.
Building reliable cybersecurity in IoT requires your business to secure the entire connected ecosystem. Device identities, access controls, network segmentation, encrypted communication, secure updates, and continuous monitoring must operate together. These protections should begin during product planning and continue until the device is retired.
This guide explains the threats affecting connected environments and the controls needed to manage them. It covers industry-specific challenges, practical security measures, implementation costs, and the business consequences of leaving IoT risks unresolved.
Why Cybersecurity Has Become Critical for Enterprise IoT
IoT for enterprises is no longer sitting on the edge in 2026. Connected devices now run factory equipment, monitor patients, track deliveries, manage buildings, and record stock movement. When one of those devices is compromised, the impact can travel quickly into day-to-day operations.
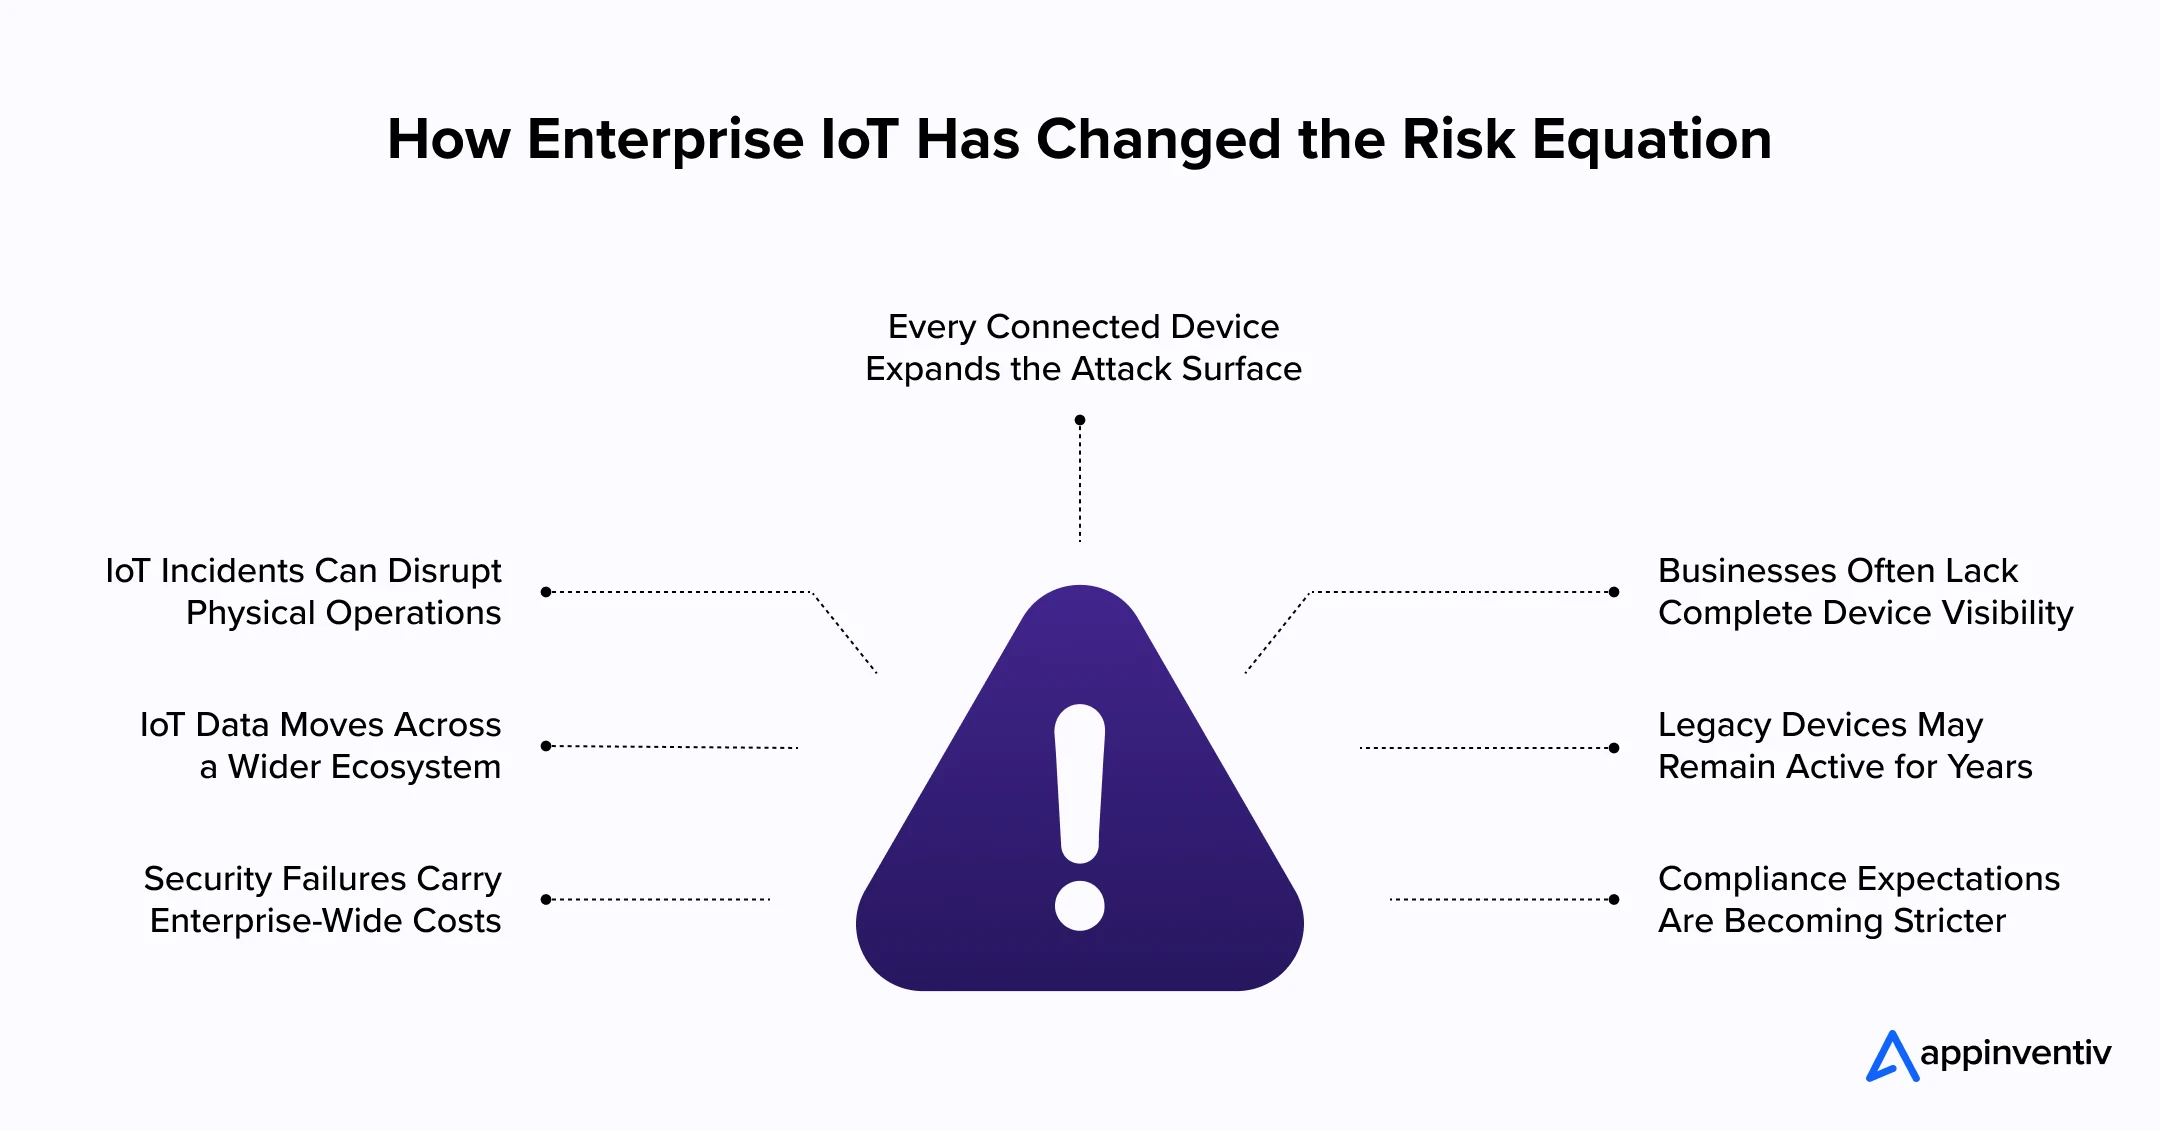
Every Connected Device Expands the Attack Surface
A business may install a sensor for one narrow task, but that sensor still creates another connection to manage. Attackers know this. They often start with the least protected device rather than attack a core system directly. One forgotten password or loose configuration can give them the opening they need.
IoT Incidents Can Disrupt Physical Operations
The damage is not always limited to data. A compromised device can stop machinery, alter equipment settings, delay a shipment, or interrupt patient monitoring. In safety-sensitive environments, the incident can put people at risk as well.
Businesses Often Lack Complete Device Visibility
Laptops and mobile phones usually pass through a central IT process. IoT equipment does not always follow that route. A department may purchase it directly, a vendor may install it, and nobody may remove it when the project ends. Before long, devices are online without a clear owner, update schedule, or support plan.
IoT Data Moves Across a Wider Ecosystem
Information collected by a device seldom stays there. It can move through a gateway, API, mobile app, cloud service, and reporting platform before someone uses it. Each transfer creates another place where the data can be exposed or changed. For this reason, Internet of Things cybersecurity must protect the entire route, not just the hardware at the starting point.
Legacy Devices May Remain Active for Years
Factories, hospitals, and utility providers cannot replace equipment as often as office computers. Some connected devices remain active for ten years or more. By then, the original vendor may have stopped releasing updates, while the device still performs an important job.
Patching brings its own difficulty. Operations teams may need to stop a production line, take clinical equipment out of service, or schedule maintenance around customer demand. So updates are delayed, sometimes for months.
Security Failures Carry Enterprise-Wide Costs
Investigation and recovery are only the first expenses. The business may also lose production hours, miss deliveries, breach customer contracts, or face regulatory scrutiny. If the incident affects a connected service used by customers, rebuilding trust can take much longer than restoring the system.
Compliance Expectations Are Becoming Stricter
A broad statement that a device is “secure” will not satisfy an auditor or regulator. Businesses need evidence. They must know what the device collects, where that information travels, who can access it, and how long the product will receive support.
That evidence depends on clear ownership and dependable records. Without them, compliance becomes a rushed search across procurement files, vendor emails, spreadsheets, and several internal teams.
Also Read: How Should Enterprises Chart DT-driven Compliance Challenges
How IoT Cybersecurity Differs From Traditional IT Security
Traditional cybersecurity measures usually protect laptops, servers, applications, and user accounts. Connected environments are harder to manage because they combine digital systems with physical equipment. Many devices also have limited processing power, run proprietary software, and remain active for years. Let’s look into how cybersecurity in IoT is different from traditional security.
| Area | Traditional IT Environment | IoT Environment |
|---|---|---|
| Assets | Laptops, servers, phones, and business applications | Sensors, cameras, wearables, controllers, gateways, and connected machinery |
| Ownership | Usually managed by a central IT team | Often shared across IT, operations, engineering, vendors, and business teams |
| Device lifespan | Replaced or upgraded regularly | May remain operational for ten years or longer |
| Software updates | Centralized updates are generally possible | Updates may be manual, vendor-controlled, or unavailable |
| Security tools | Supports standard endpoint protection | Many devices cannot run conventional security software |
| Availability | Systems can often be taken offline for maintenance | Downtime may interrupt production, care delivery, or physical services |
| Physical access | Usually kept within controlled workplaces | Devices may be deployed in public, remote, or exposed locations |
| Impact of an attack | Often limited to data and digital services | May affect data, equipment, operations, and human safety |
Types of IoT Cybersecurity Threats Businesses Must Prepare For
The cybersecurity vulnerabilities in IoT devices are not limited to weak passwords. Attackers can target the hardware, firmware, network connection, application, cloud platform, or third-party service supporting the device.
| Threat | How the Attack Happens | Likely Business Impact |
|---|---|---|
| Weak or default credentials | Attackers try factory-set, reused, or easily guessed passwords | Unauthorized access, device takeover, and movement into connected systems |
| Unpatched firmware | Known flaws remain open because updates are delayed or unavailable | Malware infection, remote access, or loss of device control |
| Botnet attacks | Criminals infect large numbers of devices and control them as one network | Distributed denial-of-service attacks, service disruption, and bandwidth misuse |
| Data interception | Information travels through unencrypted or poorly protected connections | Exposure of customer, employee, clinical, or operational data |
| Device spoofing | A malicious device pretends to be a trusted asset | False data, unauthorized commands, and access to protected services |
| API attacks | Attackers exploit weak authentication, excessive permissions, or exposed API endpoints | Data theft, account compromise, and manipulation of device functions |
| Malicious firmware | Altered or unauthorized code is installed on the device | Persistent access, hidden surveillance, and operational interference |
| Physical tampering | Someone accesses ports, storage, components, or reset controls | Stolen credentials, configuration changes, or complete device compromise |
| Supply chain compromise | Security weaknesses are introduced through vendors, components, or software dependencies | Widespread exposure across several devices or customer environments |
| Ransomware | Attackers lock connected systems or disrupt the platforms controlling them | Downtime, financial loss, delayed services, and unsafe manual workarounds |
| On-path attacks | An attacker secretly intercepts communication between devices and other systems | Stolen information, changed instructions, or falsified readings |
| Denial-of-service attacks | Devices or supporting platforms receive more traffic than they can handle | Unavailable services, device failure, and disruption to business operations |
A single attack may involve several of these methods. Stolen credentials, for example, can provide initial access, while an unpatched device helps the attacker remain undetected. Understanding how these threats connect makes it easier to choose controls that protect the whole environment.
Cybersecurity Challenges in Using IOT Across Major Industries
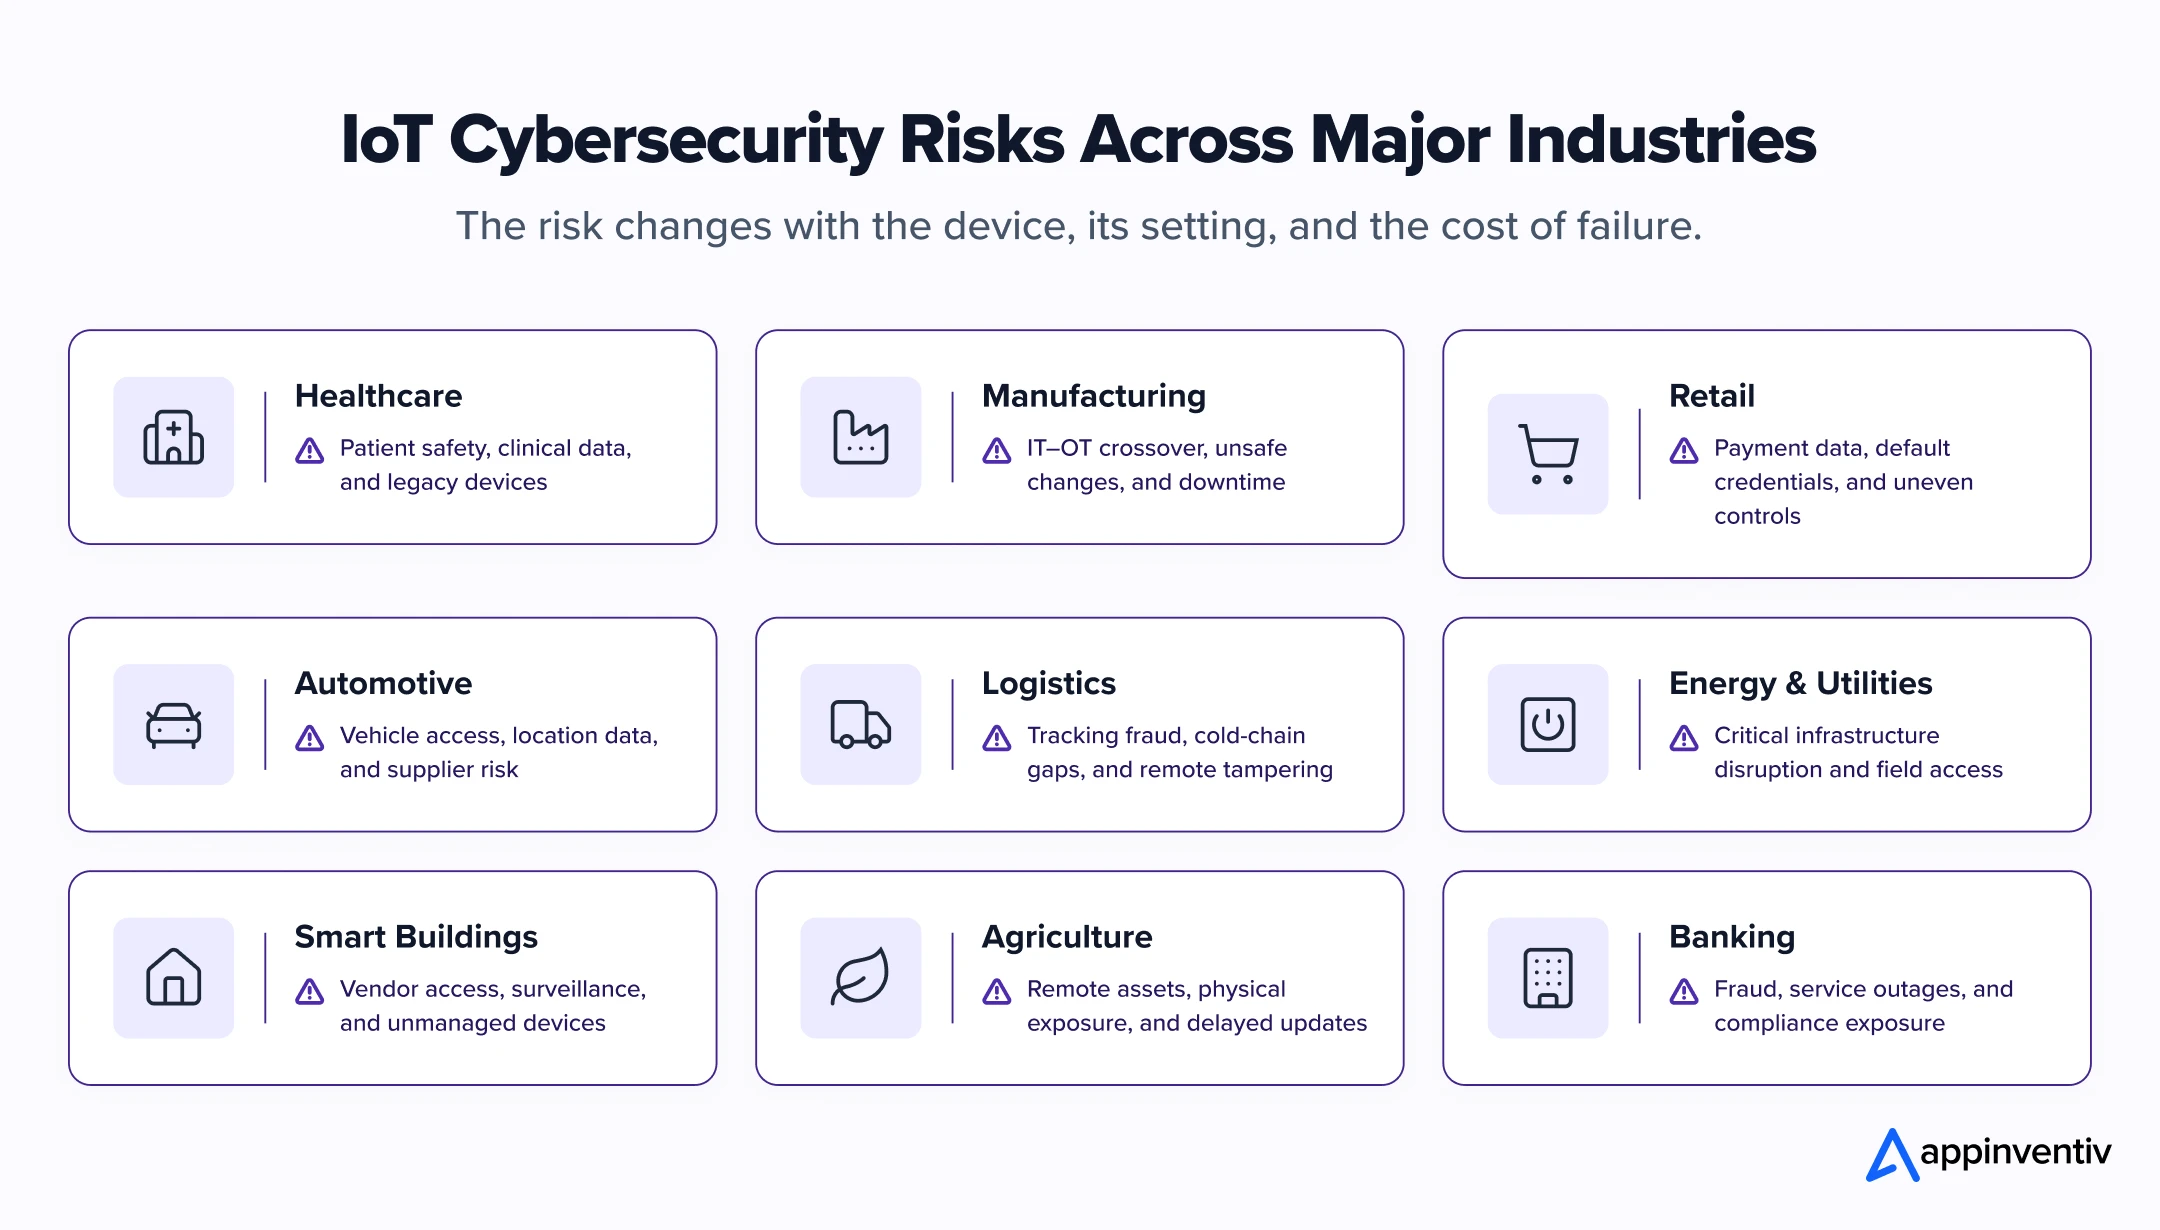
Connected devices behave differently in every business setting. A factory sensor may control machinery, while a hospital monitor may influence a clinical decision. The security approach must reflect what the device does, where it operates, and what happens if it fails.
Healthcare
Hospitals rely on connected medical devices, monitoring systems, clinical platforms, and networked equipment to support patient care. This makes cybersecurity in healthcare closely tied to both data protection and service continuity. A security incident can affect more than information; it can disrupt the systems clinicians depend on during diagnosis, monitoring, or treatment.
The challenge is that many connected devices remain in service for years. Some run older software, depend on vendor-controlled updates, or cannot be taken offline whenever a patch becomes available.
Common risks include:
- Exposure of patient and clinical data
- Disruption to monitoring, diagnosis, or treatment workflows
- Unsupported software on older connected medical equipment
- Weak authentication or excessive device permissions
- Uncontrolled access by service vendors and third parties
Manufacturing
Connected machinery helps manufacturers track output, predict equipment failure, and automate production. The problem is that many factories still run older equipment alongside newer platforms. If IT and operational networks are poorly separated, an attack can reach the production floor.
Manufacturers may face:
- Unplanned production shutdowns
- Changes to machine settings
- Damage to equipment or materials
- Theft of product designs and process data
- Safety risks for on-site workers
Also Read: Cybersecurity for Manufacturing – Building Cyber Resilience for Smart Factories
Retail
Retailers manage cameras, smart shelves, scanners, kiosks, payment terminals, and digital displays across several locations. Devices installed at different times may not follow the same security standards. Store teams may also lack the technical support needed to identify a compromised device.
The main concerns are:
- Customer and payment-data exposure
- Inconsistent security across locations
- Devices left with default credentials
- Unauthorized access to store networks
- Disruption to checkout and inventory processes
Automotive
Connected vehicles depend on sensors, onboard systems, mobile applications, cloud platforms, and external service providers. A weakness in one component can affect the wider vehicle ecosystem. Long supply chains can also make responsibility for software updates unclear.
Key risks include:
- Unauthorized access to vehicle functions
- Exposure of driver and location data
- Compromised mobile or fleet applications
- Vulnerable third-party software
- Costly recalls and regulatory action
Logistics
Logistics businesses use connected devices to track fleets, monitor cargo, scan goods, and control warehouse conditions. Many of these devices operate outside controlled premises and connect through public or unreliable networks.
This can lead to:
- Manipulated shipment or location data
- Theft of cargo information
- Interrupted warehouse operations
- Broken cold-chain monitoring
- Physical tampering with remote devices
Energy and Utilities
Utility providers rely on smart meters, grid sensors, field equipment, and remote-control systems. These assets often remain operational for decades. Taking them offline for maintenance may not be practical, even when a security weakness has been identified.
Possible consequences include:
- Disruption to essential services
- False meter or consumption readings
- Damage to operational equipment
- Unauthorized control of field systems
- Wider risks to critical infrastructure
Smart Buildings
Access systems, cameras, elevators, lighting, and HVAC equipment are increasingly connected through shared building platforms. Different vendors may manage different parts of the environment, leaving nobody with a complete view of its security.
Common issues include:
- Unauthorized building access
- Exposure of surveillance footage
- Compromised environmental controls
- Unknown or unmanaged devices
- Weak oversight of vendor access
Agriculture
Connected farming equipment may be spread across large and remote areas. Sensors, drones, irrigation controls, and livestock monitors are often difficult to inspect or protect physically. Poor connectivity can also delay updates and security alerts.
Agricultural businesses may encounter:
- Interrupted irrigation schedules
- Inaccurate crop or soil information
- Tampering with unattended equipment
- Loss of livestock monitoring data
- Disruption during time-sensitive farming periods
Banking and Financial Services
Banks use connected ATMs, surveillance systems, branch-access controls, payment infrastructure, and customer verification devices. This makes cybersecurity in banking critical across both physical and digital environments, especially where connected systems process transactions or sensitive financial data.
External maintenance access, third-party integrations, and distributed branch infrastructure add further complexity, making device visibility and access control essential.
The main risks include:
- Fraudulent transactions
- Theft of customer information
- Compromised ATMs or branch devices
- Service interruptions
- Compliance investigations and financial penalties
IoT Security Solutions for Industry-Specific Risks
Industry risks differ, but the response does not need to begin from scratch each time. The right controls create a common security base, which teams can adjust around device purpose, operating conditions, and business impact.
Start with device discovery
Build a current inventory of every connected asset. Record its location, owner, firmware version, vendor, data usage, and expected retirement date. This gives security teams a dependable view of the environment before they begin applying controls.
Assign a trusted identity to each device
Replace factory-set credentials before deployment. Give every device a unique identity through certificates, keys, or another approved authentication method. If one identity is compromised, teams can revoke it without affecting the entire fleet.
Limit where devices can connect
Place IoT assets on separate network segments and restrict unnecessary communication. A warehouse camera, for instance, should not be able to access payroll systems. These boundaries help contain an incident before it spreads.
Protect data wherever it travels
Encrypt information moving between devices, gateways, APIs, applications, and cloud platforms. Sensitive data stored on the device or within backups also needs protection. Encryption keys should remain separate from application code and device firmware.
Create a practical update policy
Rank updates according to device risk instead of treating every patch in the same way. Test critical firmware before deployment, schedule approved maintenance windows, and keep a rollback option ready. Devices that no longer receive vendor support should be isolated or replaced.
Watch for changes in normal behaviour
Many connected products cannot run standard endpoint software. Network monitoring can still identify unusual traffic, repeated login failures, unexpected destinations, or configuration changes. These signals often expose a problem before the device stops working.
Control access given to vendors
External technicians should receive named, time-bound accounts rather than permanent shared credentials. Multi-factor authentication and recorded sessions add another layer of oversight for maintenance involving critical equipment.
Plan for isolation and recovery
Teams should know how to disconnect a compromised device without bringing an entire operation to a halt. Recovery plans must cover clean firmware, trusted configurations, evidence preservation, manual operating procedures, and regulatory notifications.
Together, these IoT security solutions give businesses a workable security structure without ignoring industry realities. A hospital may prioritize patient continuity, while a manufacturer focuses on production uptime. The controls remain consistent, but their order and implementation will depend on what the organization cannot afford to lose.
IoT Security Best Practices Across the Device Lifecycle
Security decisions made before deployment are usually easier and less expensive than corrections made after thousands of devices are active. Businesses should therefore manage protection across the entire device lifecycle, from vendor evaluation to secure retirement.
| Lifecycle Stage | Action Required | Questions the Business Should Ask |
|---|---|---|
| Planning | Define the device’s purpose, data access, network requirements, and operational importance | What will the device control? What data will it collect? What happens if it fails? |
| Vendor Assessment | Review the supplier’s security practices, update policy, support period, and vulnerability disclosure process | How long will updates be available? Does the vendor notify customers about vulnerabilities? |
| Secure Development | Build authentication, encryption, logging, update mechanisms, and secure defaults into the product | Can credentials be changed? Are updates signed? Are unnecessary services disabled? |
| Testing | Test the device, APIs, mobile apps, cloud services, and network communication before release | Can attackers bypass authentication, alter data, or access another system? |
| Deployment | Replace default credentials, register the device, assign ownership, and apply network restrictions | Who owns the device? Which systems should it be allowed to reach? |
| Monitoring | Track connectivity, login attempts, configuration changes, data movement, and device health | Does current behaviour match the device’s approved purpose? |
| Maintenance | Apply tested updates, rotate keys, review access, and confirm that security settings remain active | Is the firmware current? Do vendors or former employees still have access? |
| Incident Response | Isolate affected devices, preserve evidence, maintain essential operations, and restore trusted configurations | Can the device be disconnected safely? Is a manual process available? |
| Retirement | Remove network access, erase stored data, revoke certificates, and update the asset inventory | Could the discarded device still expose credentials or business information? |
These practices should become part of procurement, engineering, operations, and security workflows. If they remain with the cybersecurity team alone, ownership gaps will return as the connected environment grows. Regular reviews also help the organization identify unsupported devices before they become an urgent operational risk.
Cost of Cybersecurity in IoT: Investment Versus the Cost of Inaction
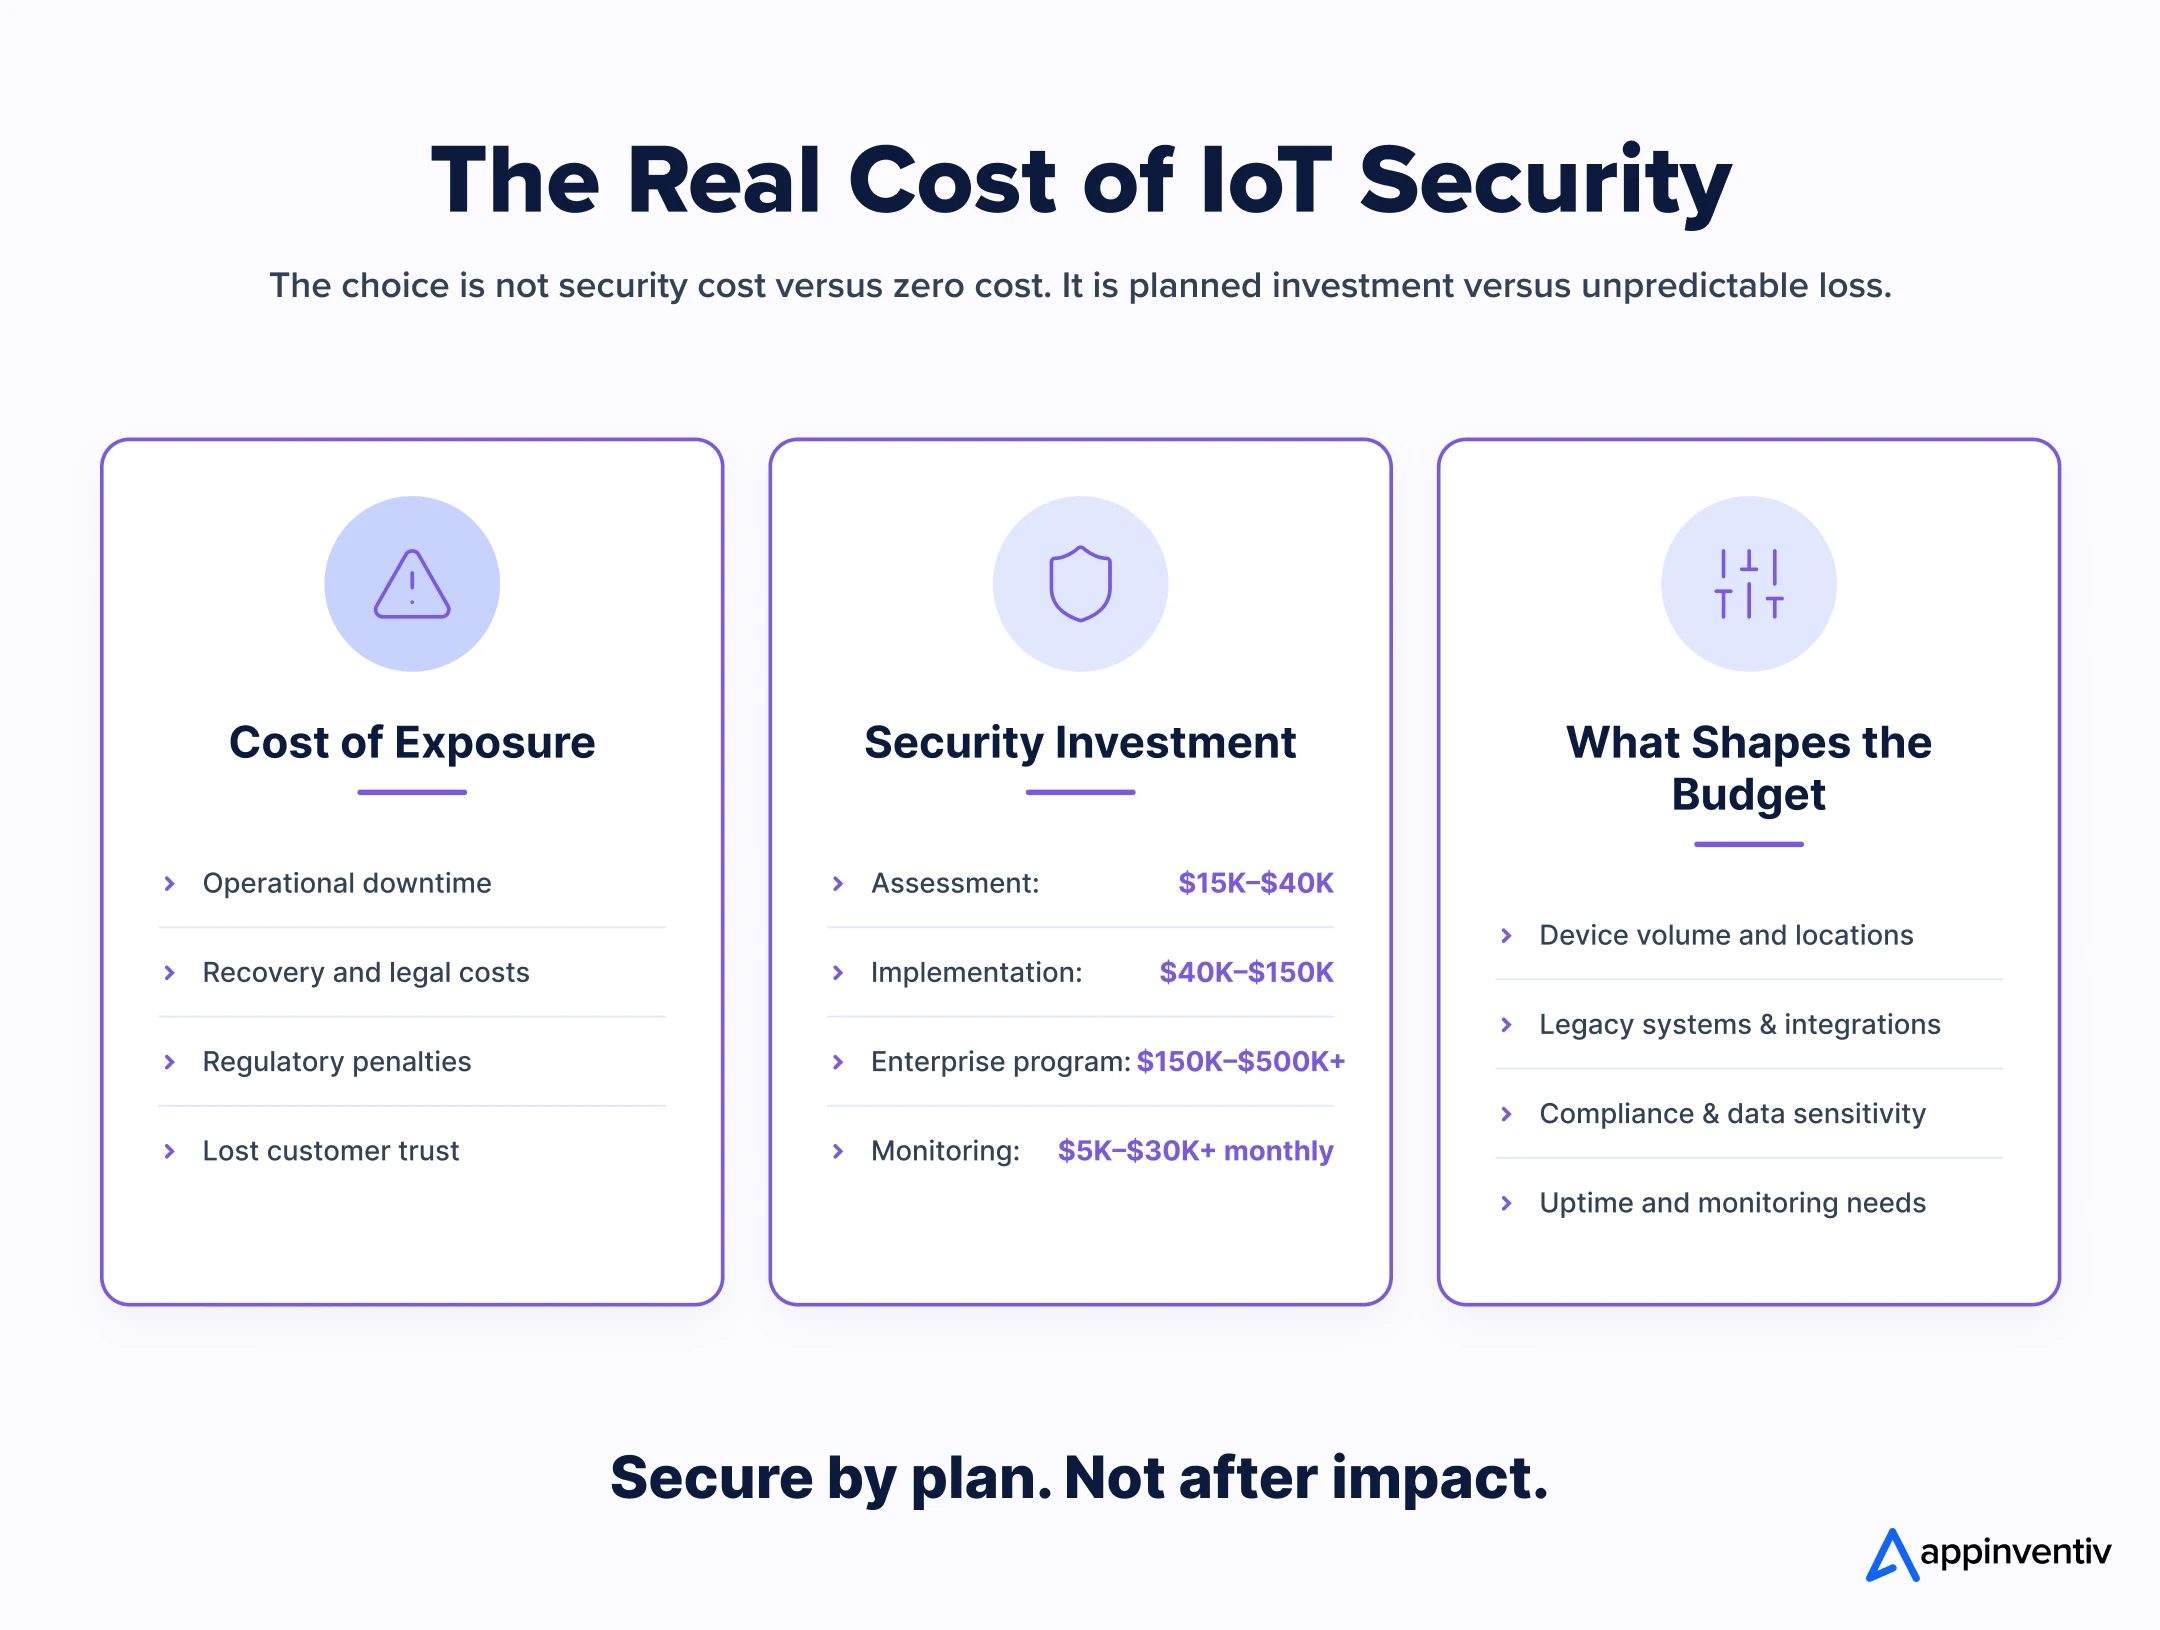
The cost of securing an IoT environment depends on more than the number of devices. Device type, operational importance, legacy infrastructure, compliance requirements, integrations, and monitoring needs all influence the final budget. However, delaying security usually creates a much larger and less predictable expense.
What an Unsecured IoT Environment Can Cost the Business
A breach does not produce one isolated bill. The financial impact builds across investigation, recovery, downtime, legal work, and delayed operations. Some losses also continue after the affected devices return to service.
The business may have to absorb:
- Revenue lost during production or service downtime
- Emergency investigation and incident-response expenses
- Device replacement and system restoration costs
- Regulatory penalties and legal claims
- Contractual penalties for missed service commitments
- Product recalls or field-service visits
- Customer notification and identity-protection expenses
- Higher insurance premiums and audit costs
- Long-term damage to customer and partner confidence
For manufacturers, utilities, hospitals, and logistics companies, operational disruption may cost more than the technical recovery itself. A security decision that saves money during deployment can therefore create a far larger liability later.
Estimated Cost of IoT Cybersecurity Services
Businesses can use the following ranges for early budget planning:
- Security assessment and risk review: $15,000 to $40,000
Covers device discovery, architecture review, vulnerability analysis, data-flow mapping, and a prioritized remediation plan. - Security testing for an IoT product: $20,000 to $60,000
May include firmware testing, API assessment, mobile application testing, cloud review, and communication-protocol analysis. - Security implementation for a growing IoT environment: $40,000 to $150,000
Can cover device identity, encryption, network segmentation, access controls, secure update workflows, and monitoring integration. - Enterprise IoT security program: $150,000 to $500,000+
Usually involves large device fleets, several locations, IT-OT integration, legacy equipment, regulatory controls, and round-the-clock monitoring. - Ongoing monitoring and support: $5,000 to $30,000+ per month
The amount depends on device volume, coverage hours, alert levels, response commitments, and reporting requirements.
These figures are indicative rather than fixed. A connected consumer product with one cloud platform will not carry the same security cost as factory equipment spread across several sites.
What Influences the Final Budget
The cost rises when the organization has:
- Thousands of devices across different locations
- Old equipment with limited security capabilities
- Several vendors and communication protocols
- Sensitive or regulated information
- Custom firmware, APIs, and cloud infrastructure
- Strict uptime requirements
- IT and operational technology dependencies
- A need for continuous threat monitoring
The cost of cybersecurity in IoT should be viewed against the value of the operations, data, and services being protected. Spending should follow business risk. A device controlling a production line or clinical process requires stronger protection than one displaying non-sensitive room information.
IoT Cybersecurity Use Cases Across Business Environments
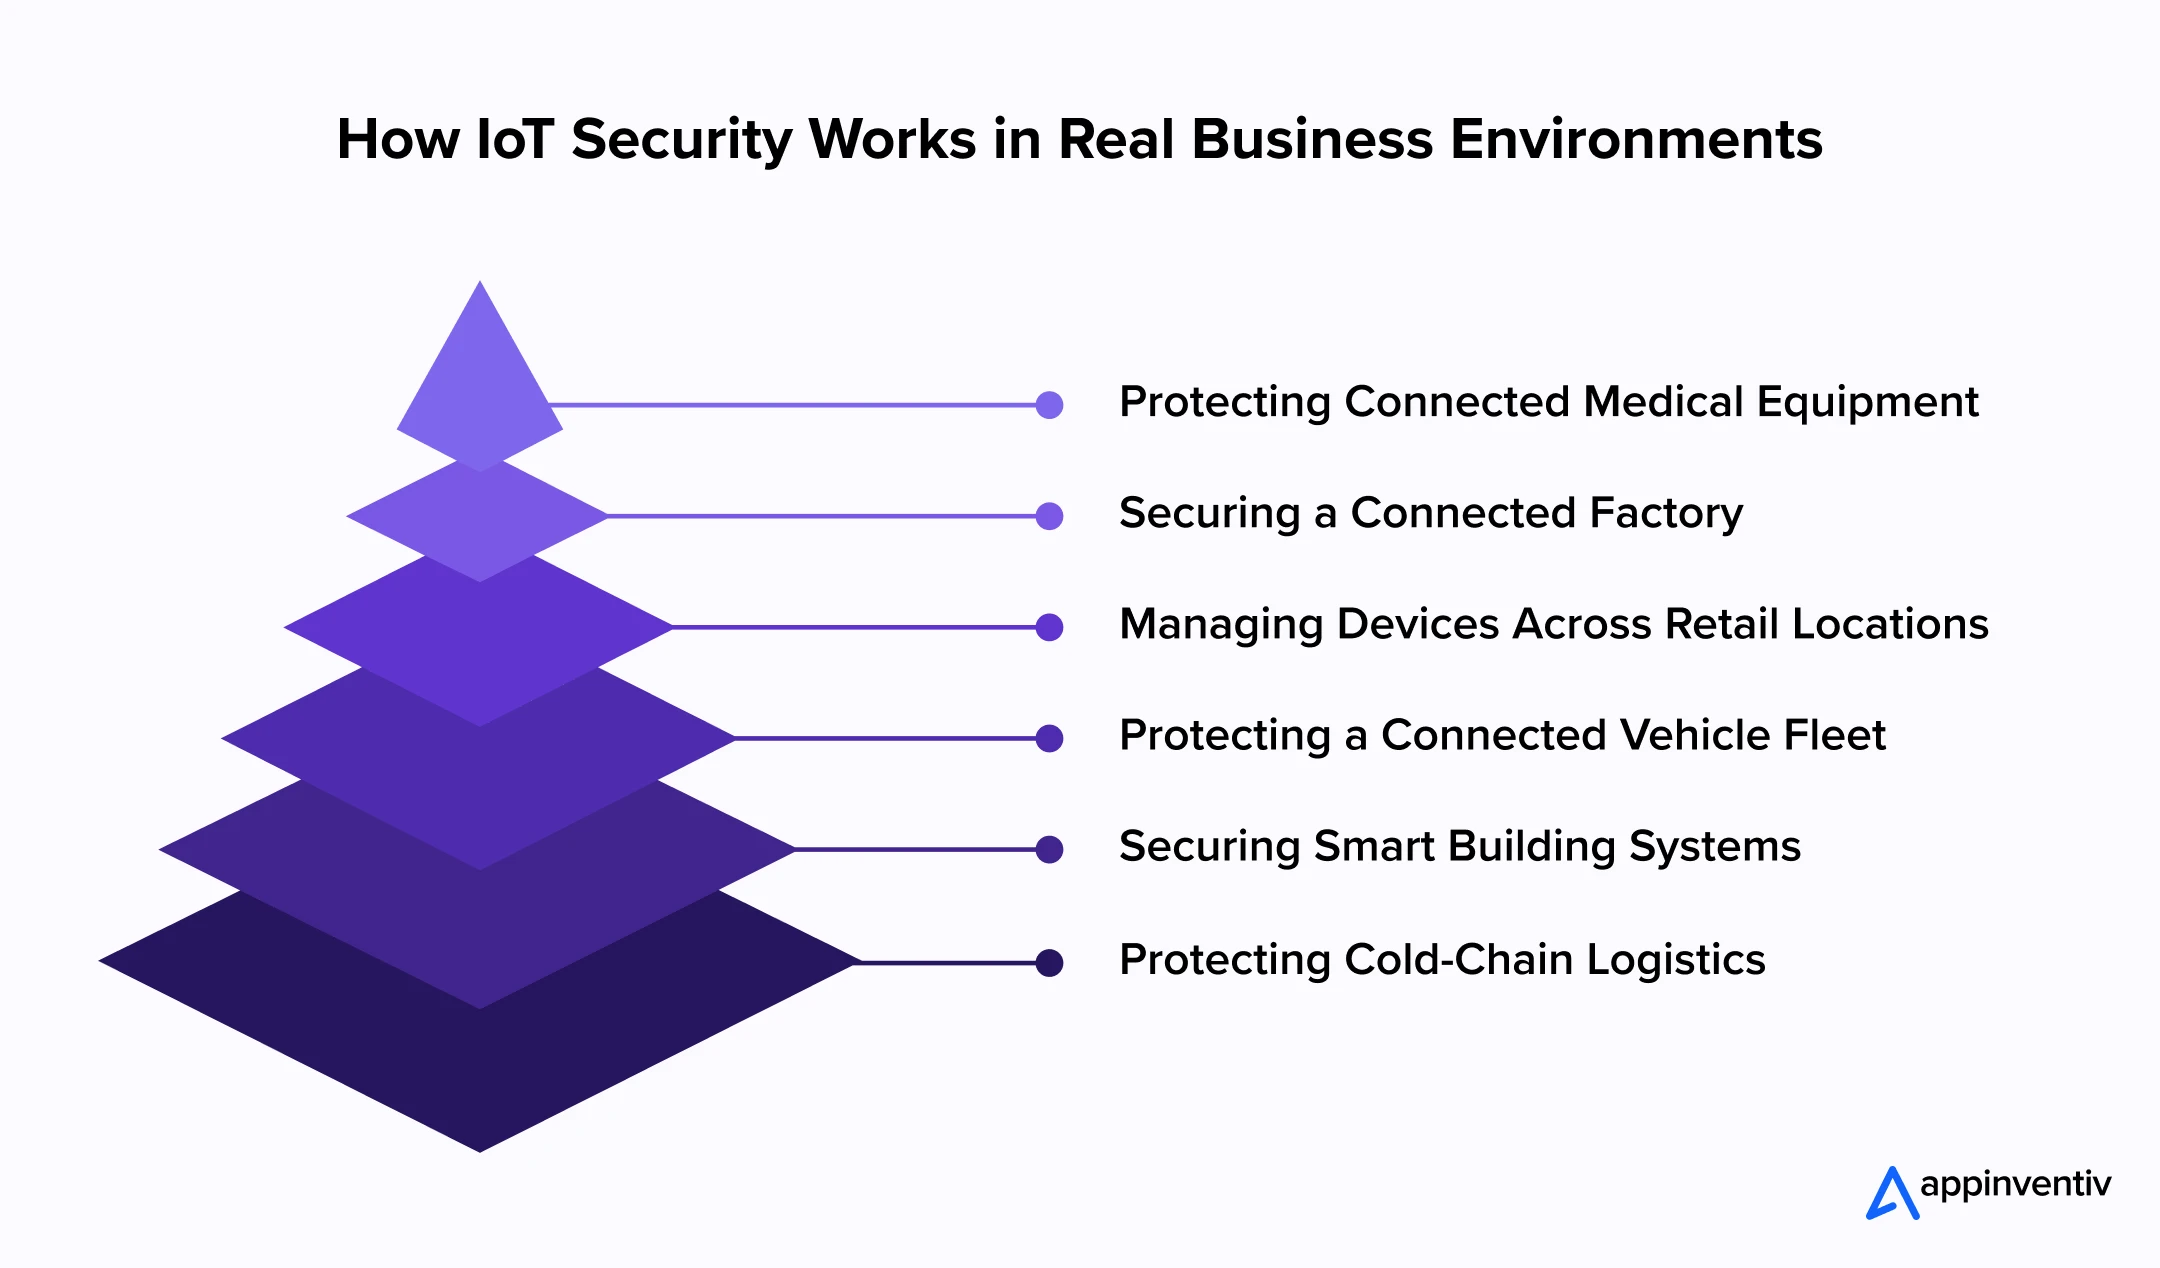
IoT security becomes easier to understand when it is viewed through everyday operations. A hospital cannot switch off patient-monitoring equipment whenever a patch appears. A factory cannot stop an entire production line because one sensor behaves strangely. Retailers face another problem: applying the same security controls across hundreds of devices and locations. The following IoT security examples show how those risks can be handled in practice.
Protecting Connected Medical Equipment
Hospitals rarely work with one generation of connected equipment. New patient monitors may operate alongside older infusion pumps, scanners, laboratory systems, and remote-care devices. Some can be updated quickly. Others cannot leave service without affecting patient care.
Each approved device should receive its own identity before joining the clinical network. From there, the hospital can restrict where it communicates. A patient monitor may need to send readings to the EHR, for example. It has no reason to connect with payroll, procurement, or unrelated administrative applications.
Good device records make the next step less disruptive. If a manufacturer reports a firmware flaw, the security team should be able to find the affected models without checking each ward manually. Clinical and technical teams can then choose a maintenance window that protects patients without leaving the vulnerability open indefinitely.
Securing a Connected Factory
Temperature sensors, vibration monitors, controllers, robots, and other connected equipment produce a steady stream of factory data. Operations teams use that information to plan maintenance, inspect output, and catch machine problems early. Still, these devices do not need free access to the corporate network.
Approved information can pass through secure gateways while production equipment remains separate from HR, finance, and email systems. This limits how far an attacker can move after compromising one device.
Suppose a vibration sensor begins contacting an unknown external server. The security team should be able to isolate that sensor without shutting down every machine connected to the line. That is the practical value of network separation. The fault stays contained while production continues.
Managing Devices Across Retail Locations
Installing one connected kiosk is simple. Managing cameras, scanners, checkout devices, digital displays, and smart shelves across an entire retail network is not.
Devices may arrive at different times, from different suppliers, with different settings. One store may update equipment on schedule while another misses several patches. Unless the retailer has one clear view of the estate, these differences remain easy to overlook.
Central IoT security management gives the business a record of each device, its location, software version, status, and assigned owner. It also helps teams spot default credentials and missed updates. When equipment is removed or a store closes, its certificates and access rights can be cancelled instead of remaining active in the background.
Protecting a Connected Vehicle Fleet
Fleet operators use telematics devices to track location, fuel consumption, driver behaviour, maintenance needs, and route performance. This information moves between the vehicle, mobile applications, and a fleet-management platform. Each handoff must come from a trusted source.
Access should reflect the person using the system. A driver needs route and journey details. A mechanic needs diagnostic records. A fleet manager may need information across the entire operation. Giving all three users identical access adds unnecessary exposure.
Vehicles should accept data and commands only from approved systems. If a telematics unit starts behaving unexpectedly, the business must be able to suspend its access without cutting off the rest of the fleet. This keeps one device problem from becoming a network-wide disruption.
Explore how we used IoT, optical gesture recognition, and secure device connectivity to build a touch-free driving application.
Securing Smart Building Systems
IoT connected buildings often depend on several contractors. One supplier maintains surveillance cameras, another manages access cards, while a third looks after lifts, lighting, heating, or ventilation. That split can leave account ownership unclear.
Shared vendor credentials are a common weak point. They may remain active between maintenance visits because each party assumes someone else will remove them.
Time-limited access provides a cleaner approach. The contractor receives permission for an approved task, the session is recorded, and the account expires after the work ends. Building systems should also remain separated from one another. A compromised camera should not create a route into access controls, lifts, or HVAC equipment.
Protecting Cold-Chain Logistics
Food and pharmaceutical companies rely on connected sensors to record temperature during storage and transport. A single reading can determine whether a shipment is released, held for review, or discarded. That makes the source and accuracy of the data important.
A trusted device identity confirms which sensor produced the reading. Encryption protects the information while it moves to the monitoring platform. Teams can also retain a clear record of when readings were collected and whether anyone changed them.
If a shipment moves outside the accepted temperature range, operations staff can review the evidence before making a decision. They are not relying on a reading that could have come from an unknown or compromised device.
These IoT cybersecurity use cases show that device protection is not only about stopping unauthorized access. Businesses also need accurate operational information, manageable recovery processes, and enough visibility to contain a problem while it is still small.
IoT Security Standards and Regulatory Requirements Businesses Must Consider
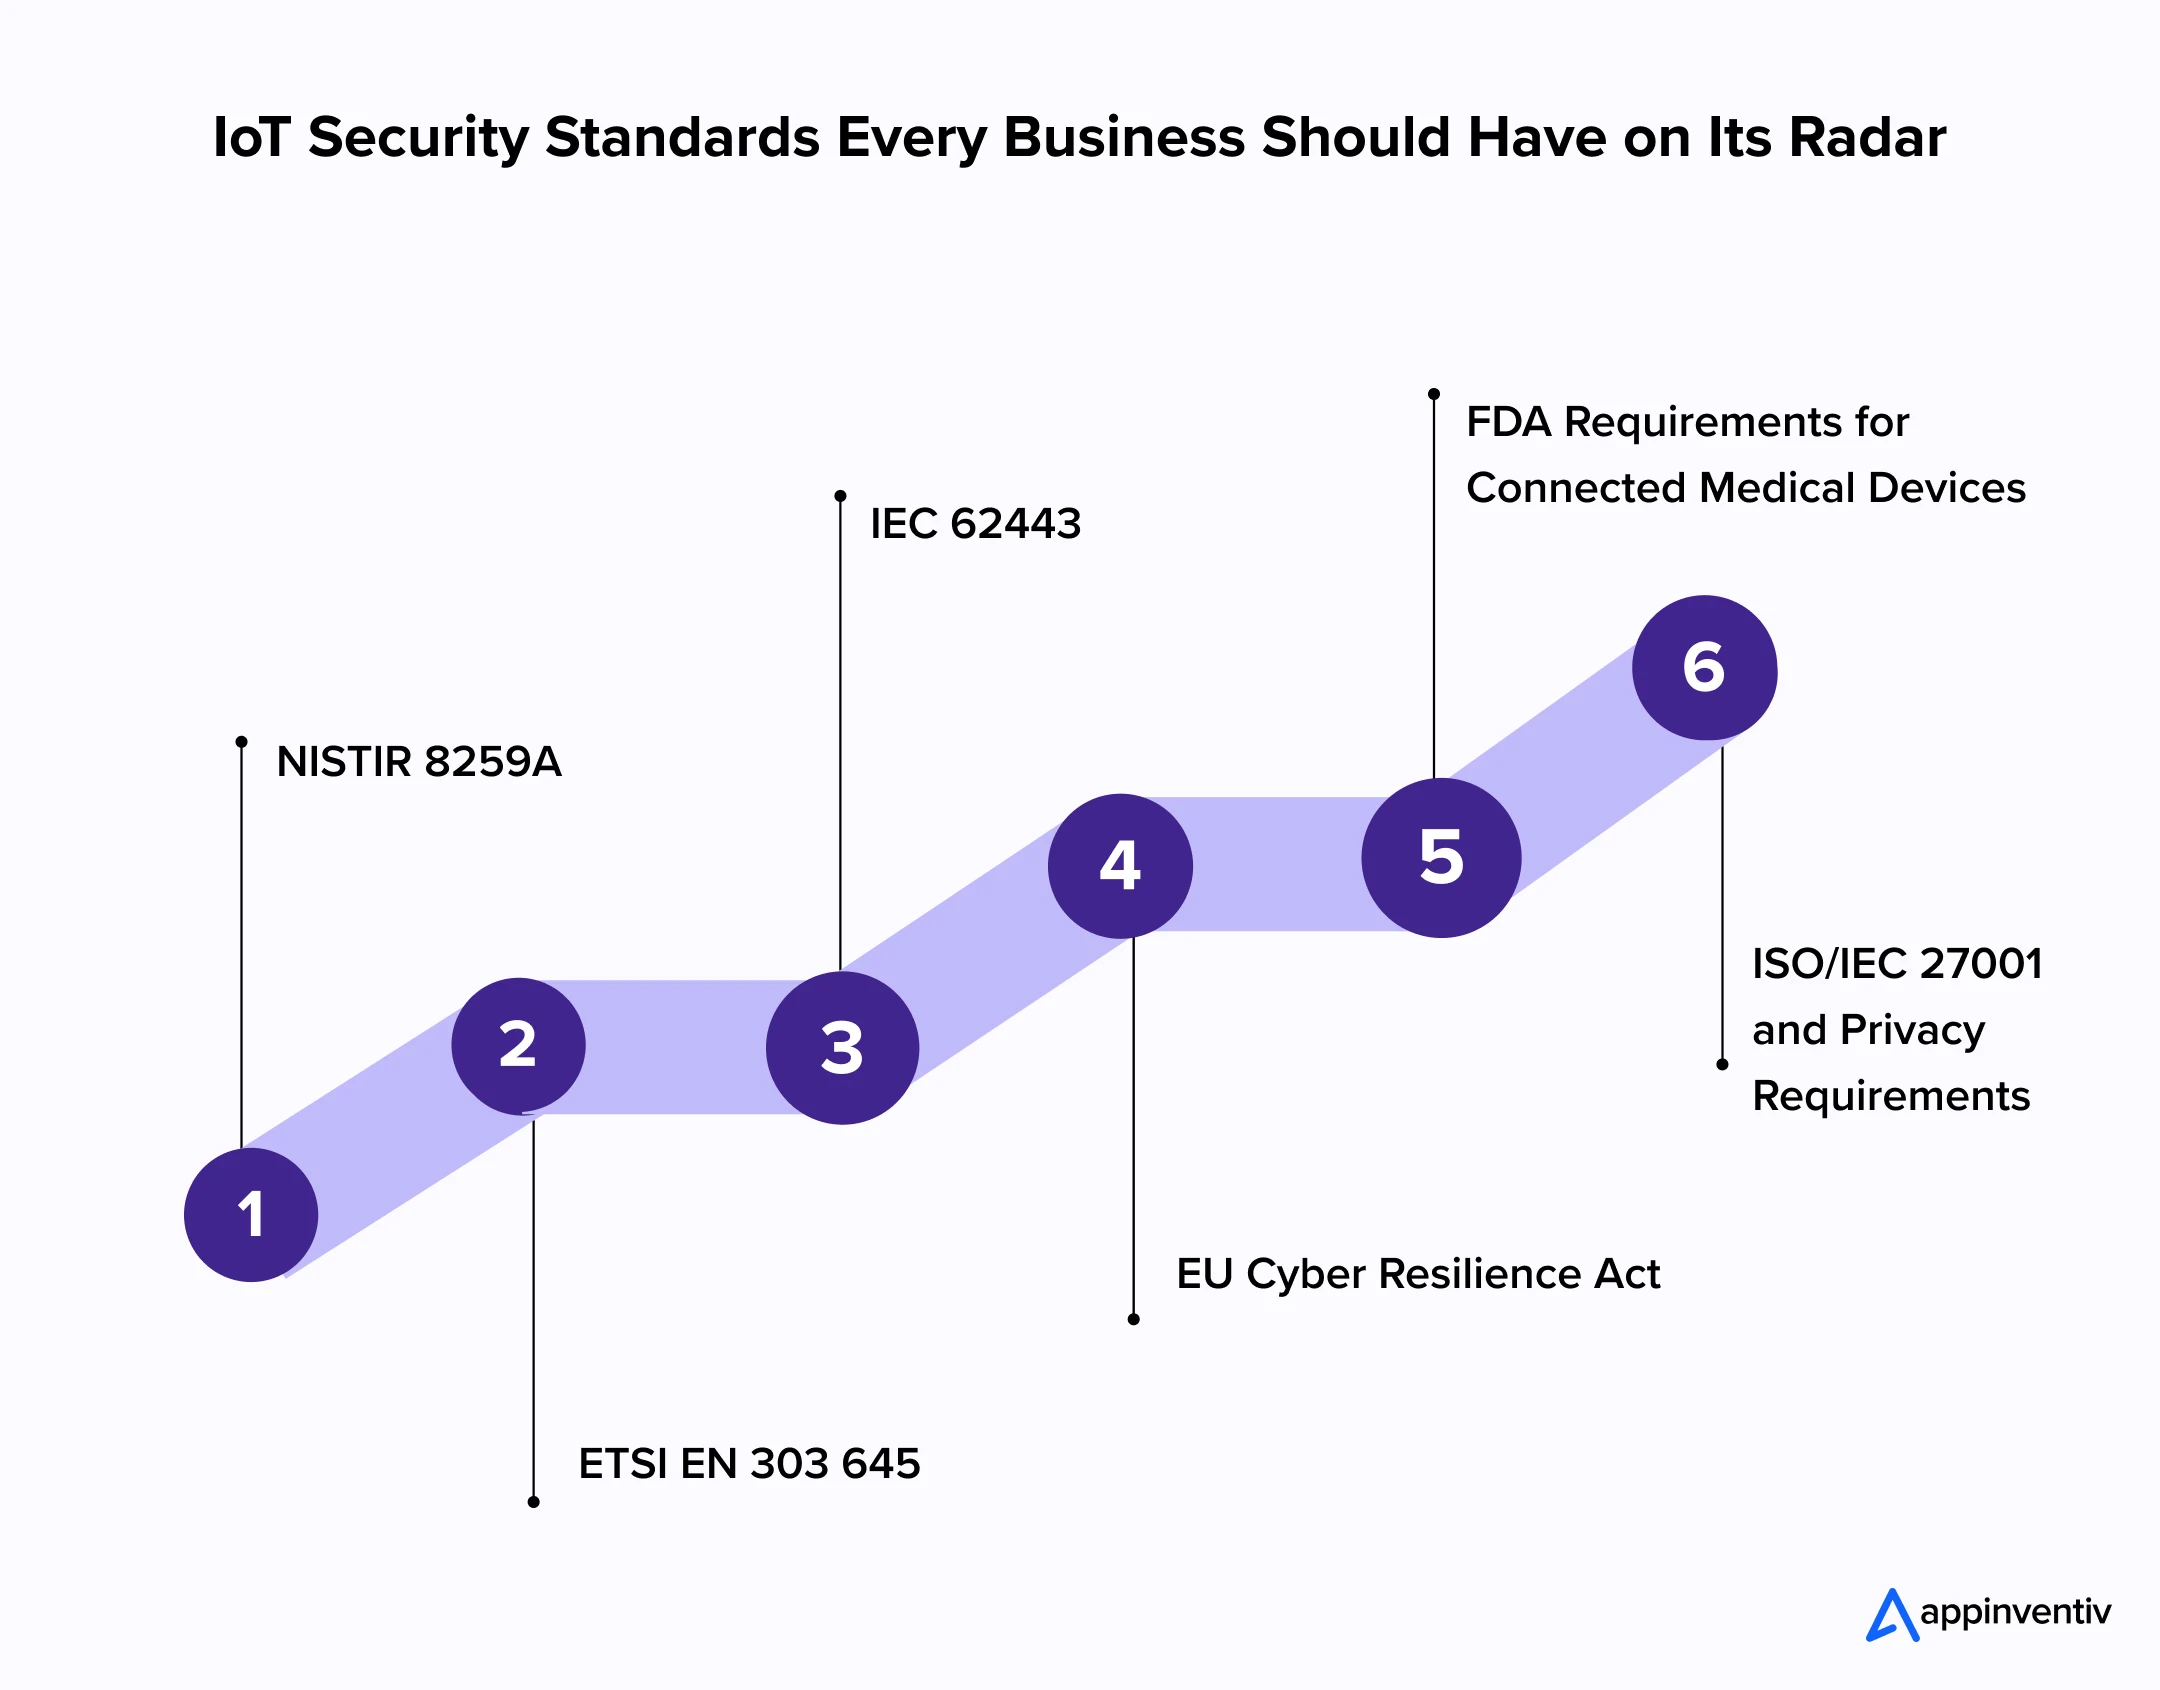
A connected product may perform well during testing and still create trouble during an audit. Security controls are only part of the requirement. Regulators, enterprise buyers, and auditors also expect evidence showing how the product was assessed, updated, monitored, and supported.
There is no universal framework covering cybersecurity in IoT devices across every market. The right requirement depends on the product, its purpose, the information it handles, and where the business plans to sell or operate it.
NISTIR 8259A
NISTIR 8259A gives manufacturers, integrators, and purchasers a baseline for reviewing device security capabilities. It is useful during product planning and procurement because it directs attention to the controls a device should support, not merely the security claims made by its supplier.
The baseline covers:
- Identifying each device clearly
- Changing and protecting device configurations
- Safeguarding information stored or transmitted by the device
- Restricting access to interfaces
- Installing trusted software updates
- Reporting the device’s cybersecurity state
NIST presents the baseline as a starting point, not a ready-made checklist for every connected product. A simple consumer sensor and an industrial controller carry different risks. Businesses still need to adjust the controls around what the device does and what could happen if it fails.
ETSI EN 303 645
ETSI EN 303 645 focuses mainly on consumer IoT products. It addresses weaknesses that appear repeatedly in connected devices, including universal default passwords, insecure communication, poor update processes, and unclear vulnerability reporting.
The standard is relevant to businesses developing products such as:
- Smart home equipment
- Internet-connected cameras
- Wearable devices
- Smart appliances
- Child-monitoring products
- Consumer health and fitness devices
For product teams, the standard provides a practical reference during design and supplier review. It can also help procurement teams ask more useful questions about credential handling, updates, data protection, and post-launch support.
IEC 62443
IEC 62443 applies to industrial automation and control systems. It is particularly relevant where connected equipment interacts with production machinery, utilities, transportation systems, or other operational technology.
Responsibility in these environments is often shared. The product manufacturer builds the component. A system integrator installs it. A service provider may maintain it, while the asset owner remains accountable for the wider operation. IEC 62443 helps those parties define their respective security roles.
The standard covers areas such as secure product development, system architecture, access control, network separation, and ongoing security work. It is not limited to the device itself. The wider industrial environment matters just as much.
EU Cyber Resilience Act
The EU Cyber Resilience Act sets mandatory cybersecurity requirements for products with digital elements. Its scope covers planning, design, development, maintenance, and vulnerability handling.
The Act entered into force on December 10, 2024. Vulnerability-reporting obligations began applying on September 11, 2026. The main obligations will apply from December 11, 2027.
Businesses planning to sell connected hardware or software in the EU should not wait until the final deadline. Product documentation, support periods, vulnerability-reporting processes, update policies, and conformity evidence can take time to prepare. These requirements may also affect supplier contracts and internal ownership.
FDA Requirements for Connected Medical Devices
Medical-device cybersecurity carries a direct safety concern. If a vulnerability changes how a connected device performs, the issue may affect more than information security. It can also affect diagnosis, monitoring, or treatment.
The FDA’s current guidance addresses secure product design, labeling, cybersecurity risk management, and the information expected in premarket submissions. The agency issued its updated final premarket guidance in June 2025.
Manufacturers also need a process for identifying and addressing vulnerabilities after a product reaches the market. This includes monitoring new risks, assessing their possible effect on patients, and communicating appropriate action to healthcare providers and users.
ISO/IEC 27001 and Privacy Requirements
ISO/IEC 27001 is not an IoT-specific standard. It is still relevant because connected products depend on a wider information environment. Cloud platforms, mobile applications, internal processes, suppliers, support teams, and user accounts all sit around the device.
An organization can use the standard to manage these information-security risks through defined policies, ownership, controls, and reviews. That wider structure matters when device information passes through several systems before reaching the business.
Privacy requirements may also apply when a connected product collects personal, location, health, biometric, or behavioural information. Businesses should have clear answers to the following questions:
- What information does the device collect?
- Why does the business need that information?
- Where will it be stored and processed?
- Who can view, change, or share it?
- How long will the business retain it?
- How can users exercise their privacy rights?
Compliance work should begin while the product architecture is still being decided. Adding consent controls, audit logs, documentation, and secure-update processes after launch is harder and usually more expensive. It also leaves the business trying to explain decisions that were never recorded in the first place.
Emerging Trends Shaping the Future of IoT Security
IoT security is entering a different phase. Keeping passwords strong and firmware current still matters, but those measures no longer cover the full problem. Device fleets are getting larger. Software supply chains are harder to trace. Regulations are also placing more responsibility on the companies that build and operate connected products.
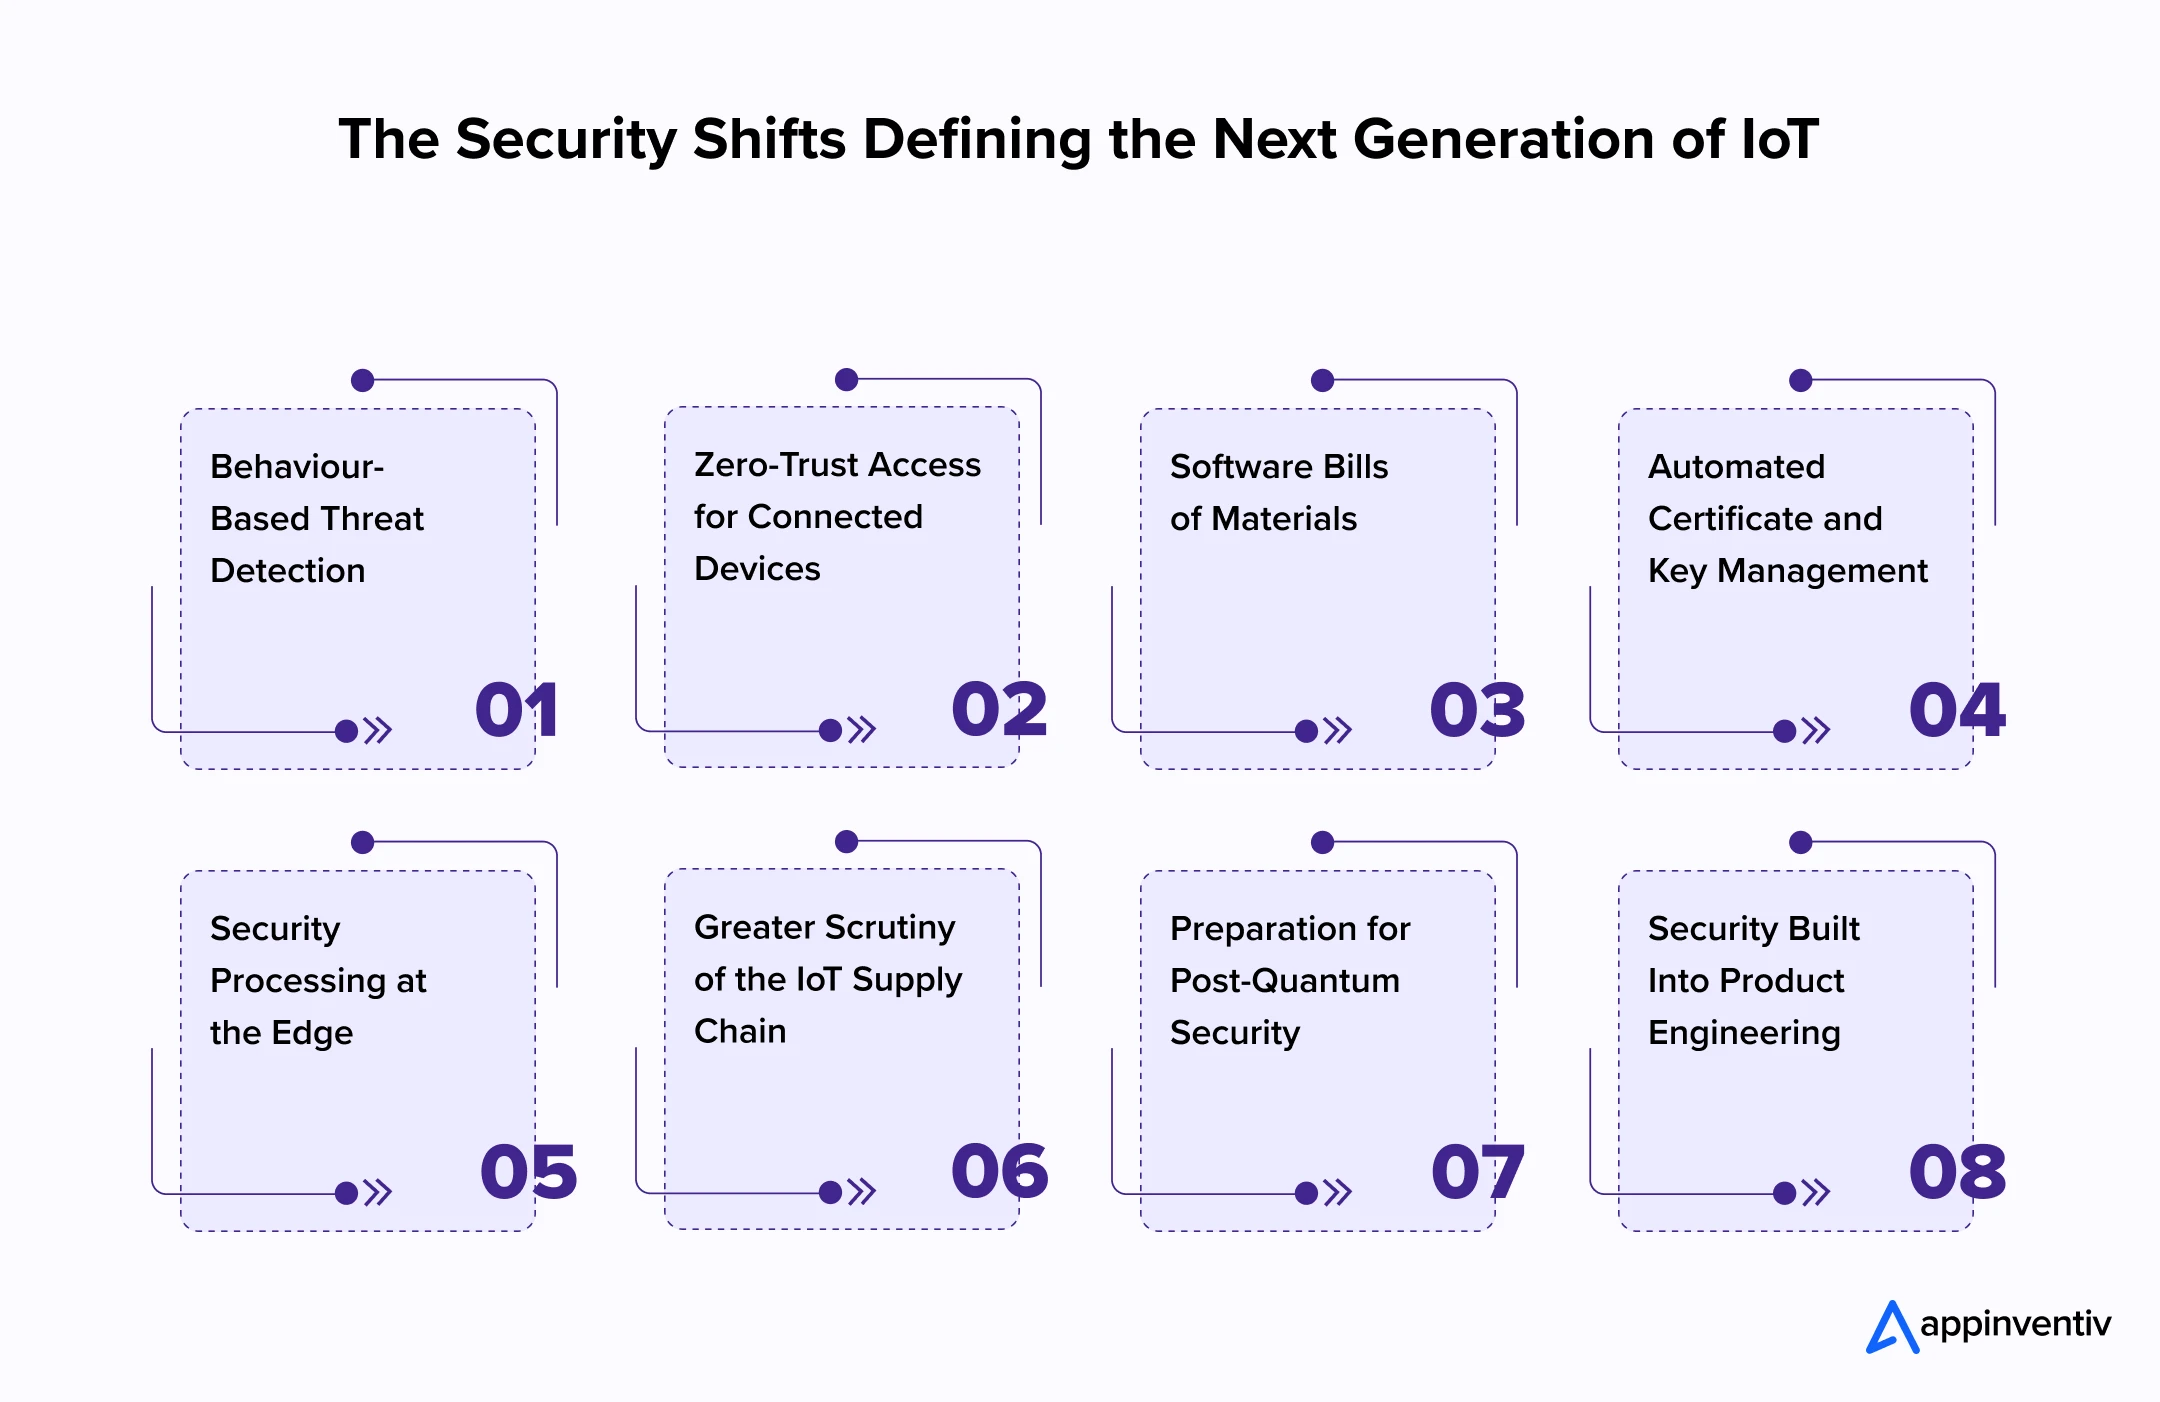
Behaviour-Based Threat Detection
Traditional tools are good at finding attack patterns they have seen before. Connected environments are less predictable. A factory controller, building camera, and medical sensor will not behave in the same way, even when they share a network.
Behaviour-based monitoring looks at what is normal for each device. A sensor that suddenly contacts an unknown server deserves attention. So does a camera that begins transferring far more data than usual. The activity may not match a known attack signature, but it still gives the security team a reason to investigate.
Zero-Trust Access for Connected Devices
Many networks continue to trust a device after its first successful connection. That is risky. The device could later run outdated firmware, use a stolen certificate, or begin making requests outside its original purpose.
Under a zero-trust model, access is checked each time. The system considers the device identity, its current condition, and the resource it wants to reach. A temperature sensor may submit readings to a maintenance platform. It does not need access to payroll, email, or customer records.
Software Bills of Materials
A connected product rarely contains software written by one company alone. Its firmware may include open-source packages, external libraries, operating-system components, and code supplied by several vendors.
This becomes a problem when one component develops a serious flaw. Without a clear record, teams may spend days trying to identify affected products. A software bill of materials, commonly called an SBOM, provides that record. It shows which components sit inside each product and where the business needs to act first.
Automated Certificate and Key Management
Manual certificate work can manage a small pilot. It starts to break down when the estate reaches thousands of devices across several sites.
Certificates expire. Keys need rotation. Devices are replaced, transferred, or removed. A compromised identity may also need to be cancelled immediately. Automating these tasks reduces the chance of forgotten credentials remaining active long after the device has left service.
Security Processing at the Edge
Not every security decision should wait for a cloud platform. The connection may be slow, unavailable, or too far from the operation that needs protection.
An edge gateway can inspect device traffic locally. If equipment begins communicating with an unapproved destination, the gateway can block that connection at the site. The security team still receives the alert, but the immediate response does not depend on a round trip to the cloud.
Greater Scrutiny of the IoT Supply Chain
The company named on the product is only one part of its security story. Hardware components, software libraries, firmware modules, cloud services, and maintenance partners may all come from elsewhere.
Procurement teams are starting to ask more direct questions. How long will the vendor provide updates? Who reports a vulnerability in a third-party component? What happens when the product reaches the end of support? These points belong in the contract, not in an email exchange after a breach.
Preparation for Post-Quantum Security
Some connected equipment stays in operation for ten or even twenty years. That creates a long planning window. Information protected today may remain sensitive long after the current encryption method becomes unsuitable.
Most businesses do not need an immediate replacement program. They do need to know which devices use encryption, how long those devices will remain active, and whether their cryptographic controls can be changed. Systems built around fixed algorithms will be much harder to update later.
Security Built Into Product Engineering
A team cannot bolt strong security onto a finished IoT product shortly before launch. By that point, hardware limitations and architecture decisions have already narrowed the available options.
Authentication, updates, encryption, logging, and recovery need a place in the original product plan. Product managers must understand the trade-offs. Engineers need clear requirements. Operations teams should know how the device will be maintained once customers begin using it.
That is where the future of cybersecurity in IoT is heading: fewer last-minute security reviews and more responsibility during product design. The change may feel slower at the start. In practice, it avoids expensive corrections after thousands of devices are already in use.
How AI Is Changing IoT Cybersecurity
The volume of IoT activity has made manual security work increasingly difficult. A large enterprise may receive traffic from thousands of sensors, controllers, cameras, gateways, and connected products. Security teams cannot review every connection or alert by hand. This is where AI in cybersecurity can take on much of the initial analysis.
AI does not replace device controls, encryption, segmentation, or secure firmware. It helps teams spot trouble sooner and decide where to investigate first.
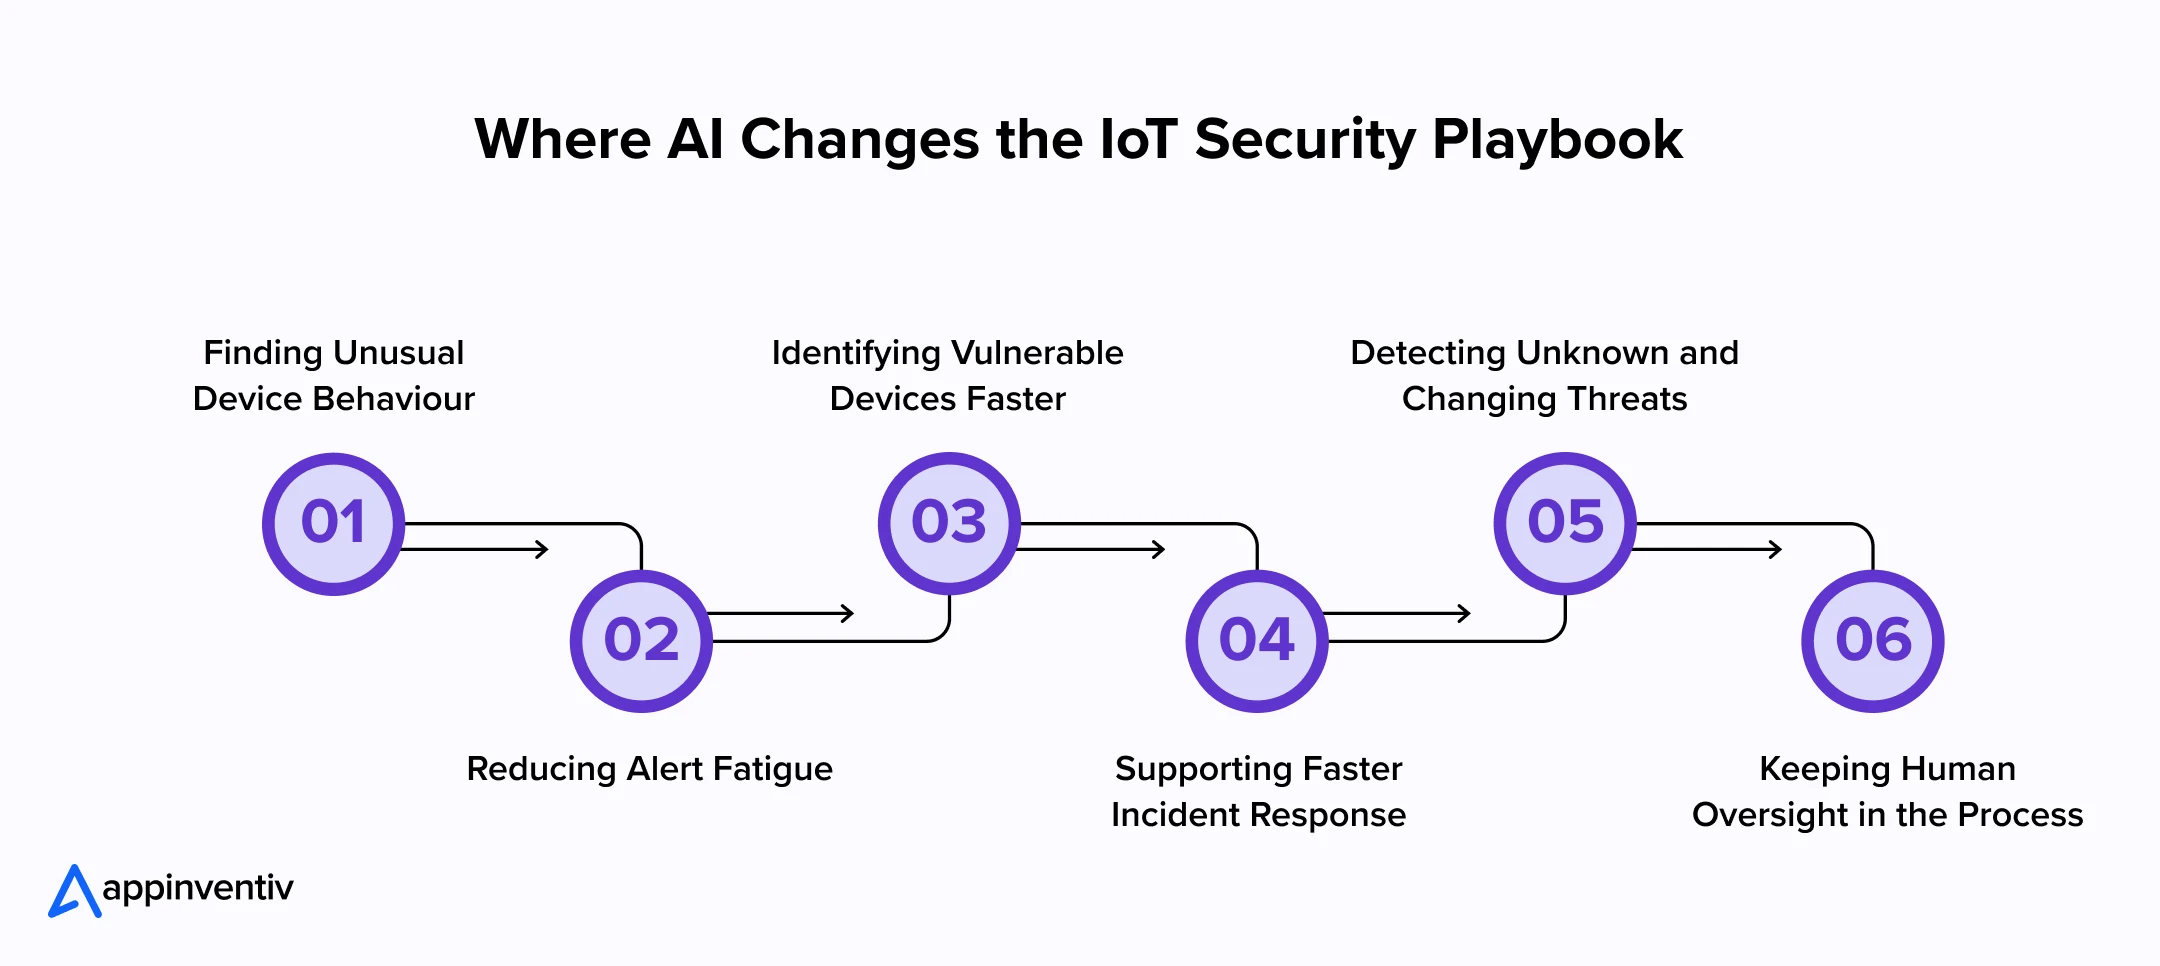
Finding Unusual Device Behaviour
Connected devices usually follow a narrow routine. A sensor sends readings at set intervals. A camera communicates with an approved platform. A controller issues a limited range of commands.
AI models can learn these patterns and flag activity that falls outside them. That could be a device contacting an unknown address, sending data at an unusual time, or making a request it has never made before. The model does not need to recognize a known malware signature. The behaviour itself raises the concern.
Reducing Alert Fatigue
IoT environments can produce a large number of low-value alerts. When teams receive too many, serious warnings become easier to miss.
AI can group related events and add context before an analyst sees them. Several failed logins, a configuration change, and an unusual outbound connection may look minor on their own. Together, they tell a different story. Bringing those events into one investigation saves time and gives the analyst a clearer starting point.
Identifying Vulnerable Devices Faster
When a new vulnerability becomes public, security teams need to know which devices are affected. That search becomes difficult when manufacturers use different product names, firmware labels, and component records.
AI can compare vulnerability information with device inventories, SBOM records, and asset data. It can then help teams locate exposed products and rank them by business risk. A vulnerable display in a meeting room does not carry the same urgency as a vulnerable controller running a production line.
Build an AI-powered IoT security model that spots unusual activity early and helps your team respond with context.
Supporting Faster Incident Response
A compromised device may need to be isolated within minutes. Waiting for several teams to review the same alert can allow the problem to spread.
AI-assisted response can recommend the next step based on the device, its role, and the systems around it. In approved situations, it may block a connection or move the device into a restricted network. Human approval should remain in place for actions that could interrupt production, treatment, transport, or another critical service.
Detecting Unknown and Changing Threats
Attackers often alter their techniques to avoid known security rules. AI-based analysis looks beyond fixed signatures and compares current activity with established patterns across the environment.
This makes it useful for cybersecurity in IoT, where devices vary widely and conventional endpoint tools may not run. It also gives teams a better chance of finding slow or unfamiliar attacks before they reach critical systems.
Keeping Human Oversight in the Process
AI can make a wrong connection, misread normal activity, or recommend an action that creates operational disruption. Connected environments leave little room for blind automation.
Businesses should define where AI can act independently and where a person must approve the response. They also need records showing why an alert was raised, what data supported the recommendation, and who authorized the final action.
The strongest approach combines AI-led analysis with firm security controls and experienced human judgment. That balance matters. Faster detection is useful, but only when the response respects the business operation behind the device.
How Appinventiv Helps Businesses Build AI-Ready IoT Security
In the era of AI, connected products need more than a standard security layer added shortly before launch. Their architecture must support trusted device identities, protected data exchange, continuous visibility, and faster investigation as the device estate grows.
As an IoT development services firm, we approach IoT security as part of the product and its wider operating environment. Our teams examine how the device, firmware, mobile application, APIs, cloud platform, and enterprise systems work together. This helps uncover risks that may remain hidden when each component is reviewed separately.
We also help businesses prepare the data and monitoring foundation required for AI-led security. That includes clean device inventories, reliable logs, clear communication patterns, and response rules tied to operational risk. Without this groundwork, AI produces more alerts but not necessarily better decisions.
Our work can cover architecture review, threat modelling, secure product engineering, API and application security, cloud protection, device-access controls, testing, monitoring, and incident planning. We shape cybersecurity for IoT solutions around the client’s industry, product maturity, compliance duties, and tolerance for downtime.
For businesses modernizing an existing connected environment, we first identify what is active, what is exposed, and what cannot be interrupted. As a dedicated cybersecurity services company, we bring security into design and development so teams do not have to rebuild critical controls after launch.
Appinventiv’s IoT cybersecurity services help enterprises combine practical security controls with AI-supported monitoring and response. The aim is straightforward: protect the connected product, keep the underlying operation stable, and give security teams enough context to act before a device issue becomes a wider business incident.
FAQs
Q. Why Is cybersecurity Important in the IoT?
A. IoT devices often connect physical operations with business applications, cloud platforms, and sensitive data. If attackers compromise one device, they may use it to reach other systems or interfere with the operation it controls.
Strong cybersecurity in IoT helps businesses protect data, maintain service availability, and prevent a device-level incident from spreading across the enterprise. It becomes particularly important when connected equipment supports healthcare, manufacturing, transport, utilities, or other safety-sensitive operations.
Q. What Are the Biggest Risks in IoT Cybersecurity?
A. The greatest risks usually come from devices that remain connected but receive little security attention. Older firmware, shared passwords, open interfaces, and weak network restrictions give attackers several ways to enter.
Common risks include:
- Default or easily guessed credentials
- Unsupported software and missed firmware updates
- Poor separation between IoT and corporate networks
- Unencrypted data transmission
- Weak API and cloud security
- Uncontrolled vendor access
- Incomplete device inventories
- Physical tampering
- Compromised third-party components
The risk grows when nobody owns the device after installation. Clear IoT security management helps businesses track each asset, its software status, and the person responsible for maintaining it.
Q. What Are the Latest Trends in IoT Cybersecurity?
A. IoT security is moving toward behaviour-based monitoring, zero-trust access, automated certificate management, edge-based threat detection, and better software supply-chain visibility. Businesses are also using SBOMs to track third-party components within connected products.
AI is becoming more useful for identifying unusual device behaviour and sorting large alert volumes. At the same time, regulators are placing greater responsibility on manufacturers to support updates, report vulnerabilities, and maintain products throughout their working life. These changes are making Internet of Things cybersecurity part of product planning rather than a task left until launch.
Q. How Should a Business Choose an IoT Cybersecurity Services Provider?
A. Start with the provider’s experience in your industry and type of connected environment. A team that understands consumer wearables may not automatically understand industrial controllers or connected medical equipment.
Before making a decision, ask:
- Does the assessment cover devices, firmware, APIs, applications, networks, and cloud systems?
- Can the team test live equipment without disrupting operations?
- Do they understand the standards and regulations relevant to your market?
- Will they help prioritize and fix findings after testing?
- Can they support monitoring and incident response after deployment?
- Does the contract clearly define data handling, ownership, and response times?
Providers offering cybersecurity for IoT solutions should explain the scope in plain terms. If the proposal relies on broad claims but does not state what will be tested, important gaps may remain unnoticed.
Q. How Much Does It Cost to Secure an IoT Environment?
A. The cost depends on device volume, architecture, industry, testing depth, compliance needs, and the amount of legacy equipment involved. A focused security assessment may cost between $15,000 and $40,000, while implementation for a growing connected environment may range from $40,000 to $150,000.
Large enterprise programs can cost $150,000 to $500,000 or more when they cover several locations, IT-OT integration, continuous monitoring, and regulated operations. These figures provide a planning range, not a fixed quote. A proper assessment is needed to understand the actual state of cybersecurity in IoT devices and set the right budget.

Fast 2-minute response, fully NDA-protected.
Ecommerce Security: A Guide to Protecting Your Commerce Stack From Modern Cyber Threats
Key takeaways: Modern commerce stacks expand attack surfaces across APIs, cloud systems, third parties, payments, and customer identities. PCI DSS 4.0.1 compliance mandates strict client-side monitoring to prevent modern web-skimming and Magecart attacks. Strong ecommerce cyber security requires layered controls across architecture, identity, data, transactions, infrastructure, and integrations. Continuous testing, threat monitoring, AI-aware controls, and…
How to Hire the Right Cybersecurity Expert for Your Business
Key Takeaways Define the business risk before choosing a security title or engagement model. Match the role to the environment, whether the priority is cloud, application, compliance, incident response, or network defense. Evaluate cybersecurity professionals through relevant scenarios, practical tasks, evidence, and references. Compare permanent, consulting, managed, and hybrid models against the coverage the business…
How to Prevent Social Engineering Attacks in the Enterprise: Types, Examples, and Defense Strategies
Key takeaways: Social engineering attacks exploit human trust, making even well-secured enterprises vulnerable to a single convincing interaction. AI is making phishing, vishing, and impersonation attacks faster to launch, harder to detect, and easier to scale. Strong verification processes are essential, especially for credential resets, financial requests, and other high-risk actions. Phishing-resistant authentication, least-privilege access,…