





Cybersecurity for Manufacturing – Building Cyber Resilience for Smart Factories
 Share -


- 01Why Manufacturing Requires a Specialized Cybersecurity Approach
- 02What Cybercrime Can Cost a Manufacturing Business
- 03Major Threats That Make Cybersecurity for Manufacturing a Business Priority
- 04Cybersecurity Challenges That Make Manufacturing Environments Difficult to Secure
- 05What an Effective Manufacturing Cybersecurity Framework Must Cover
- 06How Cybersecurity Priorities Change Across Manufacturing Sectors
- 07Cybersecurity Compliance Requirements Manufacturers Need to Address
- 08How Appinventiv Helps Manufacturers Build Cyber Resilience
- 09FAQs

Key Takeaways
- Connected machinery, cloud platforms, enterprise applications, and vendor systems have made manufacturing environments more productive but also more exposed to cyberattacks.
- Manufacturing cybersecurity must protect IT and OT together without compromising plant availability, equipment safety, or production quality.
- Ransomware, stolen credentials, legacy equipment, exposed applications, and compromised suppliers can turn a digital breach into physical and financial disruption.
- A strong cybersecurity framework requires complete asset visibility, network segmentation, controlled access, continuous monitoring, secure backups, and plant-specific incident response.
- Security priorities differ across manufacturing sectors because the operational, safety, regulatory, and product-quality consequences are not the same.
- Compliance requirements should be mapped to specific facilities, systems, products, owners, and evidence rather than treated as an audit-only exercise.
- The right cybersecurity partner should prioritize risks by their effect on production and build controls around real plant conditions.
Manufacturing has moved well beyond closed production lines and isolated factory systems. Machines now exchange data with enterprise applications, cloud platforms, industrial control systems, IoT devices, suppliers, logistics partners, and remote teams. That connectivity helps plants run faster and with greater visibility. It also gives attackers more ways to reach critical operations.
The consequences are rarely limited to lost files. An attack can stop machinery, change production settings, expose product designs, delay shipments, or create safety concerns. One stolen vendor credential or overlooked legacy device may be enough to open a path into a much larger manufacturing network.
This is why cybersecurity for manufacturing cannot follow the same playbook as conventional enterprise security. Manufacturers have to protect IT and operational technology without making production less available. That calls for a clear view of connected assets, tightly controlled remote access, network segmentation, continuous threat detection, reliable backups, and an incident response plan that has been tested against real plant conditions. The right cybersecurity solutions for manufacturing should reduce exposure without interfering with output.
This blog looks at the threats manufacturers face, what a serious incident can cost, and the controls needed across IT, OT, cloud, applications, industrial assets, and third-party connections. It also covers sector-specific requirements, cybersecurity compliance, implementation costs, and the questions businesses should ask before choosing a cybersecurity partner.
Find the gaps that could let one compromised account, application, or vendor connection disrupt production.
Why Manufacturing Requires a Specialized Cybersecurity Approach
A plant is not simply another corporate network. It brings together production machinery, industrial control systems, business applications, cloud services, connected products, remote users, and third-party tools. These systems do not carry the same risk or respond to security changes in the same way.
Consider routine patching. An IT team may update a vulnerable server, install an endpoint agent, or disconnect a device until it is safe. On the plant floor, that may not be possible. A control system could run continuously, rely on a proprietary protocol, or use an operating system that the manufacturer no longer supports. Taking it offline may interrupt an entire production run, affect quality, or introduce a safety issue.
The connection between IT and OT adds to the problem. Manufacturing execution systems share data with ERP platforms. Industrial IoT devices send performance information to the cloud. Equipment vendors log in remotely to diagnose faults and carry out maintenance. Each connection supports the business, but each can also become a route to a production asset.
For this reason, cybersecurity for manufacturing has to account for several operational realities:
- Production availability must remain central to every security decision.
- Legacy machinery may need compensating controls when direct patching is not possible.
- IT and OT assets must be discovered, classified, and monitored as part of the same environment.
- Industrial protocols need purpose-built visibility and threat detection.
- Remote vendors should receive limited, verified, and time-bound access.
- Security decisions must account for worker safety and physical processes.
- Incident response plans must put safe production recovery first.
Effective cybersecurity solutions for manufacturing must fit the way a factory works. Applying standard IT controls without understanding production dependencies can leave gaps or create fresh operational problems.
The security architecture should reflect the equipment in use, the way systems connect, the risks attached to each process, and the amount of downtime the business can tolerate.
Businesses can further partner with a manufacturing IT services provider that understands both enterprise technology and plant-floor dependencies. The provider should be able to strengthen security without introducing changes that disrupt production or create new equipment risks.
What Cybercrime Can Cost a Manufacturing Business
The ransom demand is only one line in the total cost of a manufacturing attack. Once production systems become unavailable, the business also starts paying for idle machinery, unproductive shifts, delayed orders, recovery work, and missed sales.
According to the IBM Cost of a Data Breach Report 2026, the global average cost of a data breach reached $4.99 million, up 12% year over year. The report also recorded a 56% increase in AI-driven attacks. That matters to manufacturers as they connect more intelligent systems to production and give automation tools access to operational data.
Manufacturing is already carrying a disproportionate share of the threat. The IBM 2026 X-Force Threat Intelligence Index found that the sector accounted for 27.7% of the incidents X-Force observed in 2025. It was the most targeted industry for the fifth year in a row.
Operational disruption is often the purpose of the attack, not an unintended consequence. Dragos reported that ransomware affected more than 3,300 industrial organizations in 2025. Manufacturers represented more than two-thirds of the victims.
The final bill can include:
- Production downtime: Idle machinery and unavailable control systems reduce output from the moment operations stop.
- Incident investigation: Specialists must trace the entry point, establish how far the attacker travelled, and identify every affected system.
- System recovery: IT and OT assets need to be restored, checked, and returned to service without putting production at further risk.
- Delayed commitments: Missed schedules may lead to penalties, cancelled orders, or difficult conversations with key customers.
- Product quality risks: Changes to machine settings or unavailable monitoring systems can result in defective goods and recalls.
- Intellectual property theft: Stolen formulas, drawings, source code, and product designs can undo years of research and weaken the company’s market position.
- Supply chain disruption: An incident at one plant or supplier can hold up sourcing, logistics, distribution, and downstream production.
- Legal and regulatory exposure: Compromised data or safety systems may trigger investigations, litigation, notification expenses, and penalties.
The cybersecurity risks for manufacturing companies do not disappear when the machines restart. Insurance premiums may rise. Customers can request additional security audits. Regulators and supply chain partners may also impose stricter requirements before normal business resumes.
There is no useful single figure for every manufacturer. Exposure depends on the number of plants, the value of hourly output, equipment dependencies, recovery time, regulatory duties, and supply chain complexity. Putting numbers against those factors gives leadership a clearer basis for comparing the likely loss from an attack with the cost of preventing and containing one.
Assess your exposure before downtime, recovery costs, and missed commitments start adding up.
Major Threats That Make Cybersecurity for Manufacturing a Business Priority
The most serious cybersecurity threats in the manufacturing industry include ransomware, weaknesses in legacy OT, intellectual property theft, compromised suppliers, stolen credentials, and unauthorized access to industrial devices. What makes these threats dangerous is their ability to cross from a digital system into a physical operation.
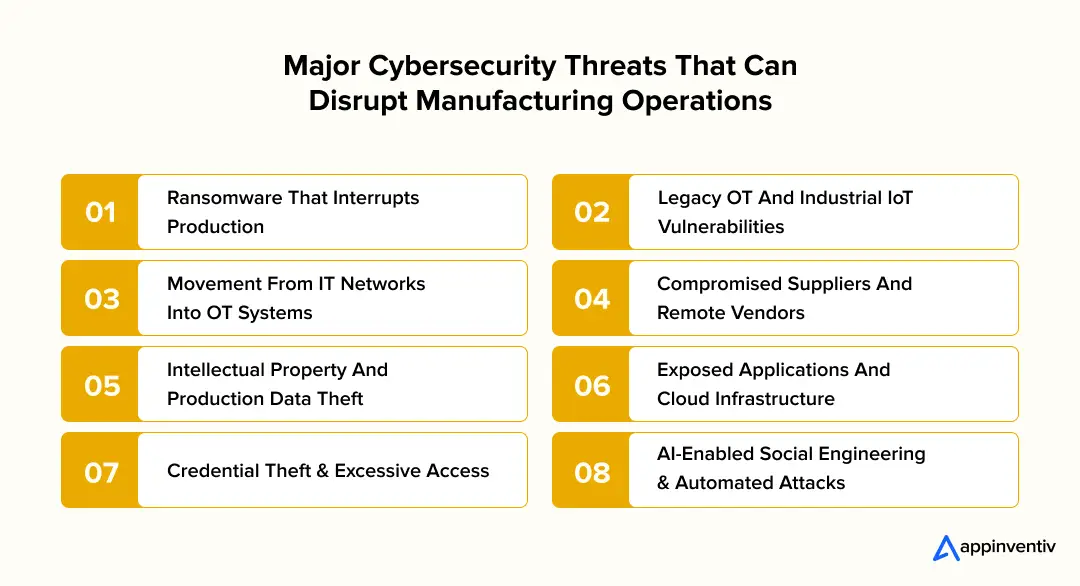
Ransomware That Interrupts Production
Ransomware does not need to reach a machine controller to bring a plant to a halt. An encrypted engineering workstation, manufacturing execution platform, inventory database, or scheduling system may be enough. Without access to specifications, material records, or safety information, the production team may have no responsible option but to stop.
Attackers understand the pressure created by every idle hour. The longer a line remains down, the harder it becomes for the manufacturer to investigate carefully rather than rush to restore access.
Legacy OT and Industrial IoT Vulnerabilities
Industrial equipment routinely stays in service for decades. Some machines still run on unsupported operating systems, old firmware, default credentials, or proprietary software that only the original vendor can update.
Newer equipment is not automatically easier to secure. Sensors, programmable logic controllers, human-machine interfaces, and industrial IoT devices often sit outside routine monitoring. Without adequate cybersecurity in IoT, a vulnerable device may remain invisible until it appears in an investigation.
Movement From IT Networks Into OT Systems
Connections between IT and plant-floor OT keep planning, inventory, quality, maintenance, and production in step. They can also give an attacker a route from a compromised mailbox, laptop, or enterprise application to a critical production system.
Weak segmentation makes that route much shorter. Malware entering through the corporate network can reach engineering workstations, production databases, or control systems before anyone has time to contain it.
Compromised Suppliers and Remote Vendors
Equipment vendors, maintenance providers, software companies, logistics partners, and material suppliers often need access to manufacturing systems. The access may be legitimate; the account or device behind it may not be.
IBM’s 2026 X-Force analysis reported that major supply chain incidents had increased almost fourfold in five years. A manufacturer can maintain strong internal controls and still be exposed by a third party with excessive permissions or a compromised account.
Intellectual Property and Production Data Theft
Product designs, formulas, source code, bills of materials, machine settings, and research data may be worth more to an attacker than customer records. Criminal groups and state-backed actors steal this material for extortion, resale, and industrial espionage.
Unlike ransomware, the theft may cause no immediate disruption. An intruder can spend weeks identifying valuable files and removing them gradually without drawing attention on the plant floor.
Exposed Applications and Cloud Infrastructure
ERP systems, supplier portals, connected product applications, mobile tools, and analytics platforms now run across public and private clouds. Common cloud security risks, such as weak access rules, poor configurations, and exposed workloads, can affect far more than the individual system under attack.
The IBM X-Force Threat Intelligence Index 2026 also recorded a 44% year-over-year increase in the exploitation of public-facing applications in 2025. Manufacturers must also address API security risks because these interfaces increasingly connect cloud applications with operational data and production systems.
Credential Theft and Excessive Access
A stolen employee, administrator, contractor, or vendor account lets an attacker walk through the front door. Because the activity appears to come from a recognized user, it may not trigger a malware alert.
Broad permissions, shared accounts, and access retained by former employees make the problem worse. With a privileged account, an attacker may change settings, disable controls, create users, and move into connected environments.
AI-Enabled Social Engineering and Automated Attacks
AI is helping attackers produce credible phishing emails, imitate trusted people, conduct reconnaissance faster, and adjust campaigns at scale. On a manufacturing network, the lure might be a maintenance request, supplier message, invoice amendment, or urgent instruction that appears to come from an executive.
There is also risk on the inside. The growing use of AI in manufacturing for predictive maintenance, automated inspection, production planning, and supply chain management gives intelligent tools access to sensitive operational data. Poor access controls or loosely governed integrations can give attackers another way in.
These cybersecurity risks for the manufacturing sector rarely appear alone. A stolen vendor credential can provide entry, weak segmentation can enable movement, and an unpatched engineering system can become the final route into production. A vulnerability-by-vulnerability review will miss that chain.
Cybersecurity Challenges That Make Manufacturing Environments Difficult to Secure
Threats describe what may attack a plant. Cybersecurity challenges in manufacturing explain why stopping those attacks is so difficult. Long equipment lifecycles, incomplete asset records, production dependencies, split ownership, and extensive third-party access all complicate the work.
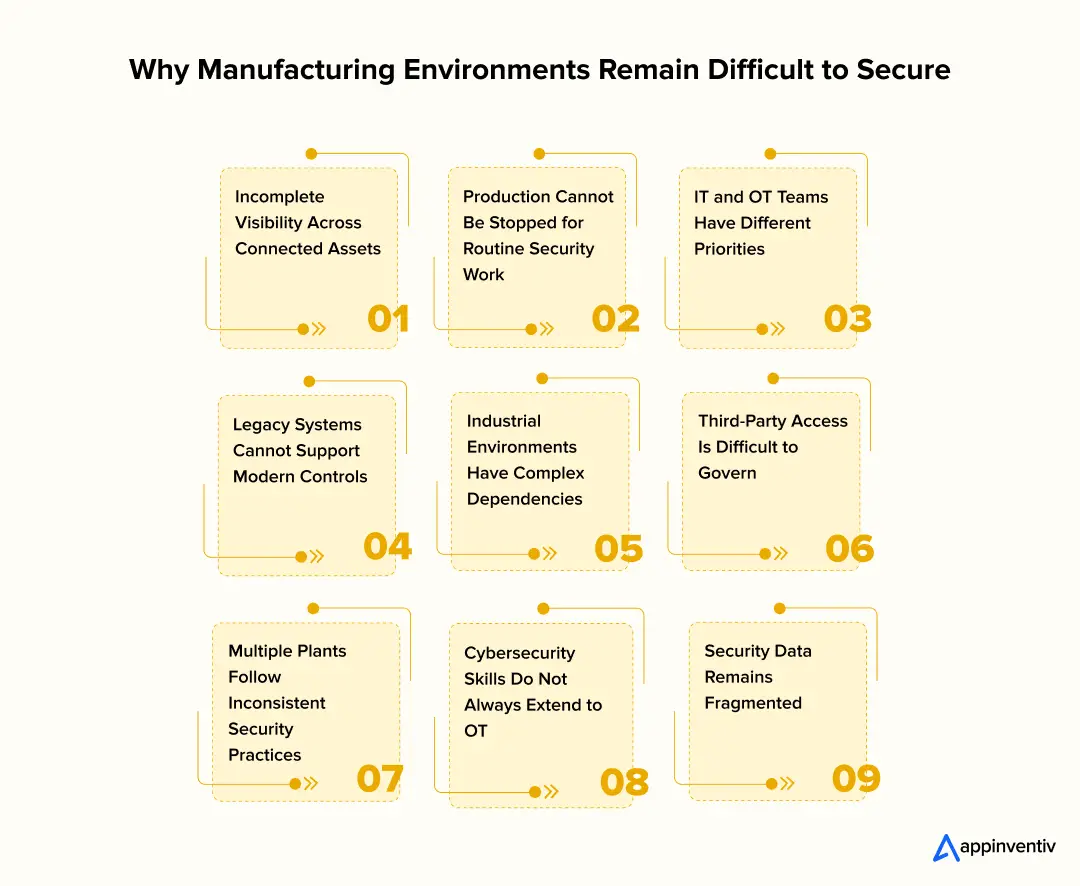
Incomplete Visibility Across Connected Assets
Many manufacturers cannot produce a current list of everything connected to the network. Undocumented machinery, temporary vendor links, industrial IoT sensors, engineering laptops, and old controllers routinely fall outside normal monitoring.
That leaves teams unable to tell which assets are exposed, vulnerable, essential to production, or connected to a sensitive process.
Production Cannot Be Stopped for Routine Security Work
Finding a vulnerability is not the same as having permission to patch it. An industrial update may need a maintenance window, vendor approval, equipment testing, and coordination with the production schedule.
Teams must then weigh a known cyber risk against the immediate operational risk of a failed update. A vulnerable system can remain online for months simply because the plant has no safe window to take it down.
IT and OT Teams Have Different Priorities
IT security teams usually focus on confidentiality, controlled access, patching, and rapid containment. OT teams carry responsibility for availability, safety, stable processes, and output.
Neither side is wrong. Trouble begins when they use different tools, terminology, and measures of risk. Decisions stall, while accountability for the space between corporate systems and plant technology remains unclear.
Legacy Systems Cannot Support Modern Controls
Older equipment may not support endpoint agents, multifactor authentication, encryption, automated scanning, or detailed logs. Some systems run on software for which no security update exists.
Immediate replacement is often too expensive or disruptive. Segmentation, restricted access, and passive monitoring must carry more of the security burden until the equipment can be retired.
Industrial Environments Have Complex Dependencies
A single production process may rely on several controllers, databases, sensors, applications, and vendor-managed services. Before isolating one of them, the response team must know what else will stop.
Disconnecting the wrong asset can halt production or interfere with a safety process. The people who understand the physical operation must therefore be involved in cyber incident decisions.
Third-Party Access Is Difficult to Govern
Maintenance providers and equipment vendors need remote access to diagnose faults and update machinery. Risk builds when the account is shared, always active, barely monitored, or able to reach more equipment than the job requires.
For every session, the manufacturer should be able to answer five questions: who connected, why, which asset they reached, what changed, and when access ended.
Multiple Plants Follow Inconsistent Security Practices
Factories in the same group are often built in different eras or inherited through acquisition. Equipment, network design, suppliers, software, and operating procedures can vary sharply from one site to another.
A control that works in one plant may be unsuitable in the next. The group still needs a common baseline, but local production conditions have to shape how that baseline is applied.
Cybersecurity Skills Do Not Always Extend to OT
Security professionals may understand enterprise networks but have limited experience with industrial protocols and physical processes. Plant engineers know the equipment intimately but may not recognize the signs of an attack.
The gap shows up in assessments, architecture, response, and recovery. Strong cybersecurity in manufacturing opeartions depends on both groups making the important decisions together.
Security Data Remains Fragmented
Corporate endpoints may be watched by one tool, cloud infrastructure by another, and the industrial network by a third. Identity, application, and physical asset data can sit elsewhere again. Analysts are left with separate alerts and little indication that they belong to the same event.
Resolving these cybersecurity challenges in manufacturing will take more than another product. IT, OT, engineering, compliance, and plant leadership need the same view of assets, risk, ownership, and recovery priorities.
Explore cybersecurity services built to protect applications, cloud platforms, connected systems, and critical operations.
What an Effective Manufacturing Cybersecurity Framework Must Cover
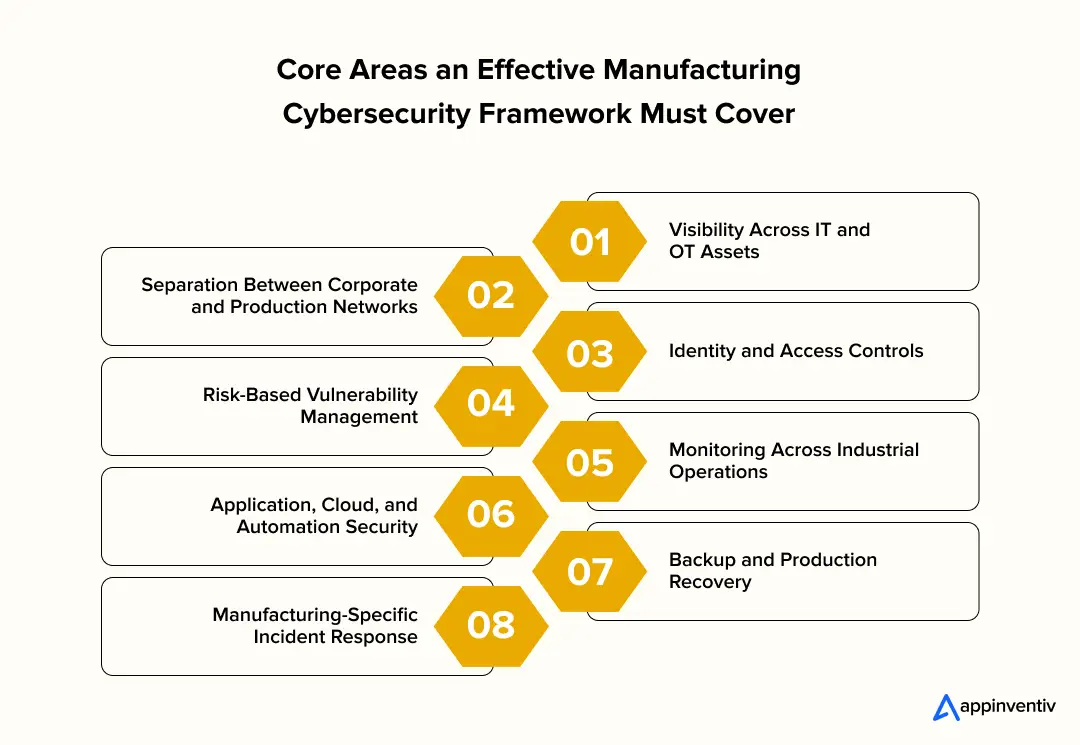
A manufacturing cybersecurity framework has to follow the production environment rather than exist as a separate IT policy. A practical cybersecurity implementation plan must cover the machinery in use, the systems around it, the people with access, and the external connections the plant relies on.
The framework will differ across facilities, but its coverage should include the following areas.
Visibility Across IT and OT Assets
The business needs a reliable record of everything connected to its environment: servers, workstations, controllers, sensors, industrial IoT devices, cloud resources, engineering tools, and vendor-managed equipment.
A list of names and IP addresses is not enough. Teams need to know what each system controls, who owns it, what depends on it, and how long production can continue without it. That is what separates a routine asset from one carrying serious operational risk.
Separation Between Corporate and Production Networks
IT and OT systems must exchange data, but they should never behave like one open network. Controlled boundaries between corporate systems, production zones, individual lines, and critical equipment can stop an incident from spreading unchecked.
Those boundaries must follow real production dependencies. Badly planned segmentation can block legitimate traffic or make equipment harder to manage. Good segmentation contains the breach while unaffected parts of the plant keep running.
Identity and Access Controls
Employees, administrators, contractors, vendors, applications, and connected machines do not need the same access. Permissions should follow a defined role and disappear when the role or task ends.
Privileged accounts deserve closer control because they can alter configurations, disable safeguards, and reach sensitive systems. Multifactor authentication, individual accounts, session monitoring, and time-limited permissions form the basis of zero trust cybersecurity for manufacturing.
Remote maintenance should meet the same standard. Every connection needs an identifiable user, a specific destination, a visible record of changes, and a clear end time.
Risk-Based Vulnerability Management
Manufacturers cannot always patch an industrial system as soon as a vulnerability is disclosed. The update may require a maintenance window, affect a vendor warranty, or break compatibility with older equipment.
The framework therefore needs a defensible approach to cybersecurity risk management that separates urgent weaknesses from those that can be managed for a limited period. Exposure, exploitability, production importance, and safety impact all belong in that decision.
If the patch must wait, network isolation, restricted access, application allowlisting, passive monitoring, or virtual patching can reduce the exposure. The risk should remain assigned and visible until a permanent fix is in place.
Monitoring Across Industrial Operations
Industrial systems are usually predictable. Controllers speak to known devices, engineering workstations perform familiar tasks, and machinery stays within established operating parameters.
Monitoring should draw attention to what does not fit: an unfamiliar connection, an unexpected command, or an unauthorized change to controller logic.
OT alerts also need context from identity, endpoint, application, and cloud systems. A strange event on the plant floor becomes far easier to investigate when analysts can connect it with a suspicious login elsewhere in the business.
Application, Cloud, and Automation Security
Factories now depend on ERP systems, MES platforms, supplier portals, mobile applications, APIs, cloud analytics, digital twins, and connected IIoT applications. A weakness in any one of them can expose production data or open a route towards operational assets.
Application testing, API protection, cloud configuration reviews, encryption, and secure development therefore belong within cybersecurity for smart manufacturing.
Automation adds another layer. Robots, controllers, sensors, and autonomous systems exchange commands with little human involvement. Cybersecurity for manufacturing automation must protect machine identities, integrations, and the instructions passing between connected equipment.
Backup and Production Recovery
Manufacturing recovery goes well beyond restoring corporate files. A plant may need clean copies of controller logic, machine configurations, engineering documents, production recipes, system images, and application data.
Those backups should be isolated from the main environment and tested regularly. The order of recovery matters too. Restarting an application before its controllers, safety systems, or data sources are validated can create a second disruption.
Manufacturing-Specific Incident Response
A standard IT response plan may say to disconnect an affected system immediately. On the plant floor, that decision could damage equipment, spoil materials, or introduce a safety risk.
Manufacturing playbooks need named roles for IT, OT, engineering, safety, compliance, legal, and plant leadership. They should address ransomware, stolen vendor credentials, altered production settings, data theft, and the loss of visibility across industrial assets.
Effective cybersecurity solutions for manufacturing connect all these areas to production risk. The framework should make three things clear: what needs the strongest protection, where an attack must be stopped, and how the plant will return to safe operation if prevention fails.
How Cybersecurity Priorities Change Across Manufacturing Sectors
Security requirements change with the product being manufactured, the equipment involved, and the consequences of an operational failure. Effective cybersecurity for the manufacturing industry must reflect these differences instead of applying the same controls to every plant.
| Industry | Main Cybersecurity Exposure | Protection Priorities |
|---|---|---|
| Life Sciences Manufacturing | Research data, laboratory systems, connected medical devices, product designs, and outside research partners all expand the attack surface. Weak cybersecurity for life sciences manufacturing can expose intellectual property and cast doubt on the integrity of test results. | Protect research and laboratory data, secure connected devices, watch third-party access, preserve audit trails, and block unauthorized changes to product specifications. |
| Pharmaceutical Manufacturing | Electronic batch records, production recipes, laboratory platforms, and environmental controls have a direct bearing on product quality. A gap in cybersecurity in pharmaceutical manufacturing may put an affected batch under review or make it unusable. | Limit access to validated systems, protect batch data, track recipe changes, preserve traceability, and test recovery against regulatory requirements. |
| Automotive Manufacturing | Automotive plants connect robotics, engineering platforms, component suppliers, embedded software, and production systems. Weak cybersecurity for automotive manufacturing can interfere with assembly, vehicle software, calibration data, and product safety. | Secure supplier connections, protect engineering data, separate robotic systems, control software changes, and monitor traffic between machines and production platforms. |
| Food & Beverage Manufacturing | Refrigeration, temperature monitoring, recipes, packaging lines, and traceability platforms are central to safe production. Poor cybersecurity for food & beverage manufacturing can spoil stock, disrupt distribution, or widen the scope of a recall. | Protect environmental controls, secure recipe and quality data, preserve batch traceability, watch production equipment, and prepare for rapid recovery. |
| Smart Factories | Machinery, sensors, edge devices, cloud platforms, AI models, digital twins, and automated systems exchange operational data continuously. That level of connectivity means smart factory security cannot rely on traditional network controls alone. | Verify device identities, secure APIs and edge infrastructure, monitor machine traffic, govern AI access, and review every connection before it reaches production. |
| Construction and Industrial Manufacturing | Mobile teams, temporary networks, shared engineering files, subcontractors, and connected site equipment keep changing who needs access. Cybersecurity in construction and manufacturing must follow users and devices as they move between projects and locations. | Use project-based permissions, secure shared designs, monitor subcontractor accounts, protect connected equipment, and remove access as soon as the work ends. |
Cybersecurity Compliance Requirements Manufacturers Need to Address
Manufacturers rarely answer to one cybersecurity rule. The applicable requirements depend on the products they make, the countries where they operate, the data they hold, and the customers they supply.
A company producing medical devices for the US market will face different obligations from an automotive supplier working with European manufacturers. Defence contractors may also need to meet conditions written directly into government contracts.
For this reason, cybersecurity compliance for manufacturing begins with identifying which standards, laws, and customer requirements apply to each facility and product line.
| Framework or Regulation | Where It Applies | What It Means for Manufacturers |
|---|---|---|
| NIST Cybersecurity Framework 2.0 Manufacturing Profile | Manufacturers looking for a risk-based security roadmap, particularly in the US | Organizes cybersecurity work around governance, asset identification, protection, detection, response, and recovery. The Manufacturing Profile adapts these outcomes to production systems and industrial risk. |
| ISA/IEC 62443 | Industrial automation and control system owners, operators, integrators, and product suppliers | Covers the security of industrial automation and control systems throughout their lifecycle. It addresses areas such as security zones, system design, product development, access control, and shared responsibility between asset owners and vendors. |
| ISO/IEC 27001 | Manufacturers that need a formal information security management system or customer-recognized certification | Requires a structured approach to information security risk, policies, responsibilities, controls, audits, and continuous improvement. It mainly supports enterprise information security and should be aligned with OT-focused controls. |
| NIS2 Directive | In-scope organizations operating in the EU, including certain manufacturers of medical devices, electronics, machinery, vehicles, transport equipment, chemicals, and food | Introduces requirements covering cyber risk management, supply chain security, incident reporting, business continuity, and management accountability. The exact obligations depend on national implementation and the organization’s classification. |
| EU Cyber Resilience Act | Manufacturers placing products with digital elements on the EU market | Requires cybersecurity to be addressed during product planning, design, development, and maintenance. Manufacturers must also manage vulnerabilities and provide security updates across the supported product lifecycle. |
| FDA Medical Device Cybersecurity Guidance | Manufacturers submitting cyber-enabled medical devices for the US market | Covers secure device design, cybersecurity risk management, vulnerability handling, labeling, and the documentation expected in premarket submissions. |
| Contractual and Customer Requirements | Automotive, aerospace, defence, pharmaceutical, semiconductor, and other regulated supply chains | Enterprise customers may require security assessments, incident notification timelines, access restrictions, audit rights, software security evidence, or alignment with named standards before approving a supplier. |
Compliance cannot be reduced to a folder of documents assembled before an audit. Policies, risk registers, and control records must match how people actually access systems and how the plant actually runs.
A workable approach to cybersecurity compliance for manufacturing connects every obligation with:
- The facility, system, product, or dataset it covers
- The person responsible for meeting it
- The technical control used as evidence
- The records required for an audit or customer review
- The incident reporting deadline
- The frequency of testing and reassessment
This mapping prevents the same control from being built several times for different frameworks. It also exposes requirements that exist on paper but are not being followed inside the plant.
How Appinventiv Helps Manufacturers Build Cyber Resilience
Improving manufacturing security is rarely a matter of adding one more tool. The real work lies in understanding how systems connect, which production processes carry the greatest risk, and where existing controls leave room for an attacker to move.
At Appinventiv, we begin by studying the complete technology environment. This includes enterprise applications, cloud infrastructure, connected products, user identities, vendor access, and the systems linked to plant operations. The assessment helps uncover exposure that may not appear in a conventional IT audit, such as an old engineering workstation connected to a critical line or a supplier account with permanent access.
The next step is to turn those findings into a practical security roadmap. Risks are prioritized according to their effect on production, safety, data integrity, and recovery. Controls are then planned around operating conditions, maintenance windows, equipment limitations, and the manufacturer’s compliance obligations. This keeps security improvements from becoming another source of disruption.
Depending on the environment, the work may involve:
- Separating corporate and production networks
- Securing applications, APIs, and cloud infrastructure
- Restricting privileged and third-party access
- Protecting connected products and industrial data
- Strengthening monitoring across IT and OT
- Testing applications and infrastructure for exploitable weaknesses
- Preparing incident response and production recovery playbooks
- Mapping controls against regulatory and customer requirements
As a cybersecurity services company, we bring these areas into one coordinated program. Manufacturers receive a clearer view of their exposure, a defensible order of priorities, and controls designed around the realities of their plants.
This approach allows cybersecurity for manufacturing to grow with the business. As new equipment, applications, suppliers, and facilities enter the environment, the security model can expand without forcing the organization to rebuild it from the beginning.
FAQs
Q. Why is cybersecurity important for manufacturing?
A. The importance of cybersecurity in manufacturing comes from the direct connection between digital systems and physical production. A breach can affect output, worker safety, product quality, intellectual property, and customer deliveries at the same time.
Manufacturers need cybersecurity to:
- Keep production systems available
- Protect designs, formulas, and production data
- Prevent unauthorized changes to machinery
- Control supplier and vendor access
- Meet regulatory and contractual requirements
- Restore operations safely after an incident
Q. How does cybersecurity work for manufacturing?
A. Cybersecurity for manufacturing protects the people, applications, networks, industrial systems, cloud platforms, and connected devices involved in production. It combines conventional IT security with controls built for operational technology.
The process generally includes:
- Discovering and classifying IT and OT assets
- Separating corporate and production networks
- Restricting user, vendor, and machine access
- Monitoring industrial communication
- Securing applications, APIs, and cloud systems
- Managing vulnerabilities around production schedules
- Preparing backups and plant-specific recovery plans
Q. What are the biggest cybersecurity risks for manufacturers?
A. The leading risks include ransomware, stolen credentials, vulnerable legacy equipment, supplier compromise, exposed applications, intellectual property theft, and weak separation between IT and OT.
These risks become more serious when:
- Asset inventories are incomplete
- Vendor accounts remain permanently active
- Industrial systems cannot be patched
- Corporate and production networks are openly connected
- IT and OT alerts are reviewed separately
- Recovery plans have not been tested
Q. Can legacy manufacturing equipment be secured without replacing it?
A. Yes. Older equipment can often be protected even when it cannot support modern security software or regular updates. The business must first understand how the equipment connects and which production process it controls.
Common safeguards include:
- Isolating the equipment within a protected network zone
- Restricting the users and systems that can reach it
- Monitoring traffic without actively scanning the device
- Allowing only approved applications and commands
- Using virtual patching where appropriate
- Documenting the risk until replacement becomes practical
Q. Which cybersecurity standards apply to manufacturing companies?
A. The relevant standards vary by sector, location, product, and customer contract. Cybersecurity compliance for manufacturing may involve NIST CSF 2.0, ISA/IEC 62443, ISO/IEC 27001, NIS2, the EU Cyber Resilience Act, FDA guidance, or customer-specific requirements.
Before selecting a framework, manufacturers should confirm:
- Which facilities and products fall within its scope
- Whether compliance is mandatory or voluntary
- Which controls apply to IT, OT, or connected products
- What evidence auditors or customers will request
- How quickly incidents must be reported
Q. How much do cybersecurity services for manufacturing cost?
A. The investment depends on plant count, asset volume, IT-OT complexity, regulatory scope, monitoring requirements, and the remediation involved. According to Appinventiv’s cybersecurity services cost breakdown, a basic implementation may cost $50,000 to $150,000, while a mid-level program may range from $150,000 to $400,000.
More complex environments may require:
- $400,000 to $900,000+: Real-time monitoring, compliance controls, and broader integrations
- $900,000 to $2 million+: Enterprise environments spanning multiple systems, business units, or locations
- Additional annual investment: Monitoring, testing, licensing, training, and incident readiness
A scoped assessment is necessary before applying these ranges to a particular manufacturing environment.
- When should a manufacturer consider managed cybersecurity support?
- Managed cybersecurity services for manufacturing are useful when internal teams cannot provide continuous monitoring or lack sufficient experience across applications, cloud, IT, and OT-linked systems.
External support may be appropriate when:
- Plants operate across multiple locations or time zones
- Security alerts require round-the-clock review
- OT security expertise is limited internally
- Vulnerability backlogs continue to grow
- Compliance reporting consumes too much internal time
- Incident-response support is needed on standby
Q. What should businesses look for in a manufacturing cybersecurity partner?
A. A suitable partner should understand production dependencies as well as enterprise security. Stakeholders should ask how the provider will assess risks associated with cybersecurity for manufacturing businesses without interrupting operations and prioritize findings according to their business impact.
The evaluation should cover:
- Experience across application, cloud, IT, and OT security
- Manual testing alongside automated assessments
- Knowledge of industrial systems and legacy equipment
- Support for compliance and audit preparation
- Practical remediation guidance and retesting
- Incident-response and recovery planning
- Clear ownership, timelines, and reporting methods

Fast 2-minute response, fully NDA-protected.
Ecommerce Security: A Guide to Protecting Your Commerce Stack From Modern Cyber Threats
Key takeaways: Modern commerce stacks expand attack surfaces across APIs, cloud systems, third parties, payments, and customer identities. PCI DSS 4.0.1 compliance mandates strict client-side monitoring to prevent modern web-skimming and Magecart attacks. Strong ecommerce cyber security requires layered controls across architecture, identity, data, transactions, infrastructure, and integrations. Continuous testing, threat monitoring, AI-aware controls, and…
How to Hire the Right Cybersecurity Expert for Your Business
Key Takeaways Define the business risk before choosing a security title or engagement model. Match the role to the environment, whether the priority is cloud, application, compliance, incident response, or network defense. Evaluate cybersecurity professionals through relevant scenarios, practical tasks, evidence, and references. Compare permanent, consulting, managed, and hybrid models against the coverage the business…
How to Prevent Social Engineering Attacks in the Enterprise: Types, Examples, and Defense Strategies
Key takeaways: Social engineering attacks exploit human trust, making even well-secured enterprises vulnerable to a single convincing interaction. AI is making phishing, vishing, and impersonation attacks faster to launch, harder to detect, and easier to scale. Strong verification processes are essential, especially for credential resets, financial requests, and other high-risk actions. Phishing-resistant authentication, least-privilege access,…