










Cloud Application Security: How to Secure Cloud-Native Apps From Code to Runtime
 Share -


- 01Cloud Application Security Across the Modern Enterprise
- 02Why Cloud Application Security Needs a Code-to-Runtime Approach
- 03Cloud Application Security Threats Enterprises Need to Address
- 04Cloud Application Security Challenges in Large Enterprises
- 05Cloud Application Security Best Practices for Enterprise Environments
- 06Cloud Native Application Security Testing Across the SDLC
- 07Cloud Application Security Solutions and Technology Stack
- 08Cloud Application Security Implementation for Enterprise Applications
- 09Benefits of Cloud Application Security Solutions for Enterprises
- 10Cloud Application Security Services for Enterprise Cloud Modernization
- 11Cloud Application Security vs Traditional Application Security
- 12Emerging Trends Shaping Cloud Application Security
- 13Why Enterprises Need an Integrated Cloud and Cybersecurity Strategy
- 14Build and Secure Cloud-Native Applications With Appinventiv
- 15FAQs

Key takeaways:
- Protect cloud apps across source code, APIs, identities, infrastructure, workloads, and runtime execution.
- Target reachable attack pathways into critical data rather than treating every vulnerability as equal.
- Embed static code analysis, dependency audits, DAST scans, infrastructure checks, and runtime protection across build pipelines.
- Eliminate technical exposure across hybrid environments, multi-cloud setups, deployment pipelines, Kubernetes clusters, and app dependencies.
- Align cloud development with cybersecurity operations to modernize application architectures without opening new security gaps.
Cloud-native applications help enterprises release features faster, support distributed teams, and run workloads across multiple cloud environments. That flexibility creates more places for security gaps to appear.
Cloud application security protects apps across their entire operating cycle. Protection covers source code, open-source dependencies, APIs, identities, cloud configurations, data, containers, and runtime workloads. Application security in cloud computing requires controls across delivery pipelines, infrastructure code, and access policies.
A strong cloud-based application security strategy starts ahead of deployment and continues past release. Development teams need clean coding practices and consistent dependency checks. Cloud operations teams need identity management, system configurations, and workload protection. Security teams need runtime visibility, active threat detection, and incident response.
This guide underscores the importance of cloud application security with a code-to-runtime view, covering the technical risks, implementation steps, and operational requirements needed to protect modern applications.
Exposed cloud workloads can connect application vulnerabilities with sensitive data, making code, identity, and runtime security equally important.
Cloud Application Security Across the Modern Enterprise
Cloud-native applications spread across microservices, databases, containers, and managed cloud services. A single business workflow crosses multiple components and cloud environments to reach its destination.
This is what makes application security in cloud computing different from legacy systems running on controlled infrastructure stacks. Microservices communicate through APIs, containers spin up rapidly, and orchestration tools shift workloads between nodes. Deployment pipelines push code updates into production on a daily basis.
CNCF found that 98% of surveyed organizations had adopted cloud native techniques in its 2025 survey. These operational patterns alter how development teams manage security risks. Access relies on identities, service accounts, API keys, and workload permissions. Multi-cloud deployments introduce additional configurations and access rules across teams.
The shared responsibility model establishes clear boundaries between platform vendors and internal teams. Cloud providers protect hardware and physical networks, but companies remain accountable for application code, data, identities, configurations, and running workloads.
What Makes Cloud Application Security Different
The characteristics of securing cloud applications originate directly from this distributed and constantly changing architecture.
- Distributed systems: Security controls must protect connected microservices instead of a single application stack.
- Shifting workloads: New containers and temporary cloud resources start during routine deployments and traffic spikes.
- Ephemeral infrastructure: Short-lived workloads terminate prior to traditional security scans completing their work.
- API-driven communication: Internal and public APIs create multiple pathways between core applications and external microservices.
- Third-party dependencies: Open-source packages and third-party integrations widen the application supply chain footprint.
- Rapid releases: Automated security checks must integrate into build pipelines without delaying production deployments.
- Identity-based access: Access policies and workload permissions govern interactions across users, services, and databases.
- Constant configuration changes: System settings update continuously through infrastructure code, automated scripts, or administrative consoles.
- Multi-cloud visibility: Defense teams require unified operational oversight across AWS, Azure, Google Cloud, and private datacenters.
Why Cloud Application Security Needs a Code-to-Runtime Approach
Production security controls alone cannot deliver complete cloud application security, since vulnerabilities often enter earlier in the development lifecycle. Unsafe packages, leaked credentials, and bad configurations often slip into early build stages. Cloud application security requires active verification across every step from code to production runtime.
Code → Dependencies → APIs → IaC → CI/CD → Cloud environment → Workloads → Runtime → Monitoring → Response
Securing Applications During Development
Code security checks start inside developer environments and pull request workflows. Static analysis scanners audit custom source code for dangerous programming flaws. Software composition analysis tools spot vulnerable open-source packages and hidden project dependencies. Dedicated secrets scanners catch exposed access keys, API tokens, and private credentials in commits. Native integrations embed these security scans straight into daily code reviews and developer tools, a core part of enterprise application security.
Securing Deployment and Cloud Configurations
Security verification extends directly into continuous integration and automated deployment pipelines. Infrastructure scanners evaluate Terraform files, CloudFormation scripts, and Kubernetes manifests for security flaws. Build pipeline controls protect system credentials, compiled app artifacts, and production deployments. Container image scanners detect known vulnerabilities and risky configurations inside base system layers. Policy checks flag excessive identity permissions, public storage buckets, and open network pathways.
Securing Applications at Runtime
Runtime protection monitors live application behavior across deployed cloud environments. Telemetry tools connect application requests to underlying workloads, user identities, APIs, and system events. Threat detection systems spot unusual process executions, privilege escalation attempts, and active exploit vectors. Automated response mechanisms immediately isolate compromised workloads, revoke user tokens, and block malicious traffic. This continuous visibility model protects enterprise apps across every stage of the application lifecycle.
Cloud Application Security Threats Enterprises Need to Address
Cloud application security threats span source code, identities, internal APIs, cloud resources, deployment pipelines, and third-party services. The table below details critical risks requiring operational focus across enterprise environments.
| Threat | Typical cause | Potential impact | Primary control |
|---|---|---|---|
| Cloud misconfiguration | Incorrect policies or settings | Data exposure | CSPM and IaC |
| Insecure APIs | Weak authentication or validation | Unauthorized access | API security |
| Identity abuse | Stolen credentials or excessive permissions | Privilege escalation | IAM, RBAC, MFA |
| Vulnerable dependencies | Unpatched libraries | Supply-chain compromise | SCA |
| Secrets exposure | Keys in code or pipelines | Account takeover | Secrets management |
| Container vulnerabilities | Unsafe images or configurations | Runtime compromise | Container security |
| CI/CD compromise | Weak pipeline controls | Malicious deployments | DevSecOps |
| Shadow IT | Unmanaged applications | Unknown attack surface | Discovery and governance |
| Zero-day attacks | Unknown app vulnerabilities | Rapid compromise | Runtime detection |
Cloud Misconfiguration and Configuration Drift
Unsafe storage settings, open network rules, default credentials, and broad access roles expose cloud environments without source code flaws. Configuration drift introduces new vulnerabilities through live infrastructure updates following initial deployment.
Security teams require continuous scanning tools to identify system settings drifting away from baseline security standards. Wiz found that 54% of cloud environments had exposed VMs or serverless instances containing sensitive information, one of many cloud security risks enterprises face today.
Insecure APIs and Third-Party Integrations
Application programming interfaces connect business applications directly to users, internal services, commercial partners, and third-party platforms. Missing identity checks, weak authorization rules, unchecked inputs, and absent rate limits expose critical enterprise functionality.
External OAuth connections create additional exposure through third-party applications receiving broader access permissions than business operations require. Palo Alto Networks reported that 41% of surveyed organizations experienced a surge in API attacks in 2025.
Identity Abuse and Excessive Privileges
Enterprise environments depend on user logins, service accounts, workload identities, and temporary access keys. Single compromised identities with broad permissions open access pathways across connected databases and cloud resources.
Strict identity policies, role controls, multi-factor authentication, and minimum required permissions restrict attacker lateral movement. Palo Alto Networks found that 53% of surveyed organizations cited lenient IAM practices as a top cloud security challenge in 2025.
Software Supply Chain and Dependency Risks
Open-source packages and commercial app libraries comprise most modern application source code today. A compromised software dependency can expose multiple internal systems that rely on the affected package.
Deep nested dependencies complicate risk management, and application teams frequently miss hidden packages executing inside production workloads. Google Cloud found that third-party software exploitation accounted for 44.5% of observed initial access vectors in H2 2025.
Also Read: Transforming Legacy Systems with Cloud Migration: The Whys and Hows
Container, Kubernetes, and Runtime Exposure
Containerized environments, often the result of a broader software modernization strategy, introduce operational risks through unpatched base images, broad cluster roles, exposed secrets, and unsafe runtime configurations. Build pipelines create targeted entry points through unauthorized actors capturing deployment credentials or tampering with app build files.
Shadow IT and Unmanaged Cloud Applications
Business departments frequently adopt external cloud application tools without requesting formal security evaluations. Unsanctioned applications store sensitive enterprise data and connect to core services through active identity permissions. Lacking a central software inventory, security operations teams overlook unmanaged tools and the underlying access rights tied to them.
Cloud Application Security Challenges in Large Enterprises
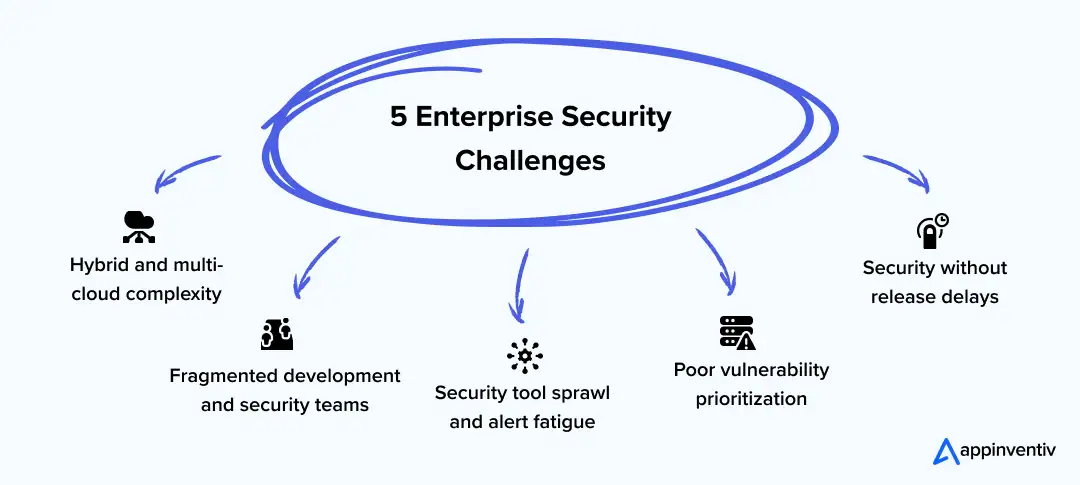
Cloud application security challenges grow alongside expanding application fleets, development teams, cloud platforms, and app releases. Operational teams must maintain uniform protections without slowing down daily application delivery.
Managing Security Across Hybrid and Multi-Cloud Environments
AWS, Azure, Google Cloud, private datacenters, and on-premises systems run on different security policies, a contrast explored further in our on-premises vs cloud comparison, identity providers, and monitoring tools. Disjointed management systems create operational friction for defense teams attempting to maintain baseline controls. Centralized asset inventories and shared policies are what make cloud-based application security achievable with uniform governance across diverse deployment environments.
Connecting Development, Cloud, and Security Teams
A code vulnerability impacts runtime cloud workloads, but isolated departments often see limited portions of the total risk. Fragmented communication channels delay threat remediation and obscure operational accountability across teams. DevSecOps practices unite application development, infrastructure operations, and cybersecurity workflows into shared management pipelines, often powered by DevOps automation. Unified tracking and explicit task ownership allow teams to trace active risks from source code straight into production.
Reducing Security Tool Sprawl and Alert Fatigue
Disconnected scanning tools for SAST, SCA, CSPM, API security, and workload protection generate duplicate alerts and conflicting threat severity scores. Development groups need to consolidate overlapping app tools and correlate operational telemetry across the application lifecycle.
A cybersecurity solution provider can help enterprises align these controls across development and security operations. Correlated security telemetry provides analysts with clear context prior to taking incident remediation steps
Also Read: How Much Does Cyber Security Cost in 2026? Enterprise TCO, Cost Drivers, and ROI Breakdown
Prioritizing Exploitable Risks Over Raw Vulnerability Counts
Total vulnerability counts reveal very little about true operational risk or business exposure. Threat severity shifts based on public internet exposure, active exploit code availability, system criticality, access rights, and accessible data assets. Risk-focused prioritization guides development effort toward resolving specific security flaws that form real attack vectors.
Appinventiv Insight: In a typical banking modernization program, moving a monolithic payments platform to microservices creates multiple security paths across APIs, containers, IAM roles, CI/CD pipelines, and cloud databases. A code vulnerability alone does not show whether attackers can reach sensitive payment data. Security teams need to connect the vulnerable component with its exposed interfaces, permissions, workloads, and reachable assets before assigning remediation priority.
Maintaining Security Without Slowing Release Velocity
Continuous deployment cycles render manual code audits and slow security gates impractical for teams. Automated security checks must execute directly inside build pipelines using transparent release policies. Critical risk discoveries can automatically block app builds, and lesser vulnerabilities move into structured remediation workflows. This balanced policy maintains rigorous security verification without interrupting core business release velocity.
Cloud Application Security Best Practices for Enterprise Environments
Enterprise cloud application security best practices focus on visibility, access control, secure delivery, data protection, and runtime monitoring.
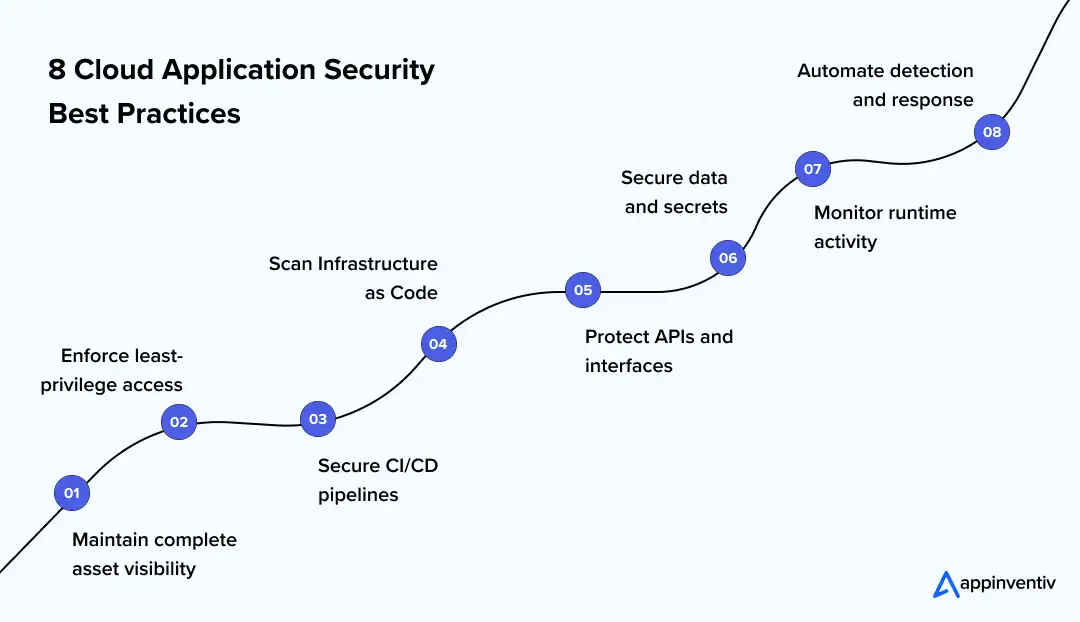
Establish Complete Application and Asset Visibility
Security teams must maintain a unified inventory covering code repositories, microservices, APIs, third-party libraries, cloud resources, and running workloads, all core to strong cloud-native platform capabilities.
Apply Zero-Trust Access and Least Privilege
Access policies must strictly enforce role-based access, multi-factor authentication, and minimum required permissions for human logins and service identities. System administrators should audit privileged access rights routinely to revoke stale credentials and dormant service keys.
Integrate Security Into CI/CD
Development pipelines require embedded static analysis, dependency scanning, and secrets detection tools running automatically during daily builds. Enforcing strict release gates for high-severity vulnerabilities blocks flawed code before deployment into live environments.
Secure Infrastructure as Code
Infrastructure scanners must evaluate Terraform files, CloudFormation templates, and Kubernetes manifests prior to resource provisioning. Policy-as-code rules systematically prevent misconfigured storage buckets or broad network rules from deploying into active accounts.
Protect APIs and Application Interfaces
Security controls require discovery mechanisms for public and internal APIs, paired with strict token validation and access checks. Enforcing request rate limits and strict payload validation prevents interface exploitation and automated abuse attempts.
Protect Data and Secrets
Sensitive data requires strong encryption protocols both during transit across networks and at rest inside database stores. Application development teams must store API tokens, cryptographic keys, and database passwords inside dedicated secrets vaults with automated credential rotation.
Also Read: AI Data Security Platform Development: A CIO’s Guide to Securing Enterprise AI
Continuously Monitor Runtime Environments
Centralized monitoring platforms must aggregate application logs, cloud infrastructure events, and container activity across operating nodes. Real-time behavioral analysis identifies abnormal process executions, unauthorized privilege escalations, and suspicious outbound network traffic.
Automate Detection, Prioritization, and Response
Security teams should evaluate vulnerabilities by mapping internet exposure against asset criticality and the availability of active exploits. Automated remediation scripts can fix routine misconfigurations immediately, while critical security alerts automatically trigger dedicated incident response workflows.
Cloud Native Application Security Testing Across the SDLC
Cloud native application security testing must track the application across development, deployment, and runtime stages. Distinct operational phases expose different threat vectors, requiring specialized security controls throughout the application lifecycle.
| SDLC Stage | Security Testing |
|---|---|
| Planning | Threat modeling |
| Coding | SAST and secrets scanning |
| Dependencies | SCA |
| Build | Container and image scanning |
| Infrastructure | IaC security |
| Pre-production | DAST and API testing |
| Deployment | Configuration validation |
| Runtime | CWPP and runtime detection |
| Production | Continuous monitoring |
SAST and Secure Code Analysis
Static application security testing analyzes source code without executing the program. Scanners detect injection vulnerabilities, unsafe functions, hardcoded secrets, and access control flaws early in development workflows.
SCA and Dependency Verification
App composition analysis audits direct and transitive open-source dependencies for known vulnerabilities, license risks, and outdated packages. Dependency scans evaluate application software libraries, package management files, and container base components, a routine part of secure cloud application development.
DAST and API Security Testing
As part of cloud-native application security testing, Dynamic Application Security Testing evaluates running applications from an external perspective. Container scanning evaluates image registries for vulnerable application packages, unsafe configurations, and risky base layers. Dynamic scans identify runtime behavior flaws invisible to static code analysis. API security tools validate authentication mechanics, authorization policies, payload inputs, endpoint exposures, and operational response traffic.
IaC and Cloud Configuration Testing
Infrastructure as Code testing reviews Terraform scripts, CloudFormation templates, and Kubernetes manifests prior to deployment. Automated checks identify public storage resources, excessive access rights, exposed services, and policy violations before provisioning active cloud infrastructure.
Also Read: Cloud Data Migration – Adopting the Right Strategy and Best Practices
Container and Kubernetes Security Testing
Container scanning, a core part of cloud native application security testing, evaluates image registries for vulnerable app packages, unsafe configurations, and risky base layers. Kubernetes testing audits cluster role permissions, workload isolation settings, exposed services, and access routes to sensitive system assets.
Continuous Runtime Validation
Runtime security controls verify live application behavior against baseline operational expectations. Security tools monitor running workloads, system processes, network connections, identity requests, and application activity for exploitation indicators. Real-time telemetry delivers live visibility that pre-production testing tools cannot provide.
Cloud Application Security Solutions and Technology Stack
Enterprise cloud application security solutions combine distinct security controls across development, cloud infrastructure, and runtime. Each technology targets a specific risk; app teams could build stacks based on application architecture and deployment environments.
| Security Capability | Purpose | Typical Technologies |
|---|---|---|
| Identity security | Control access | IAM, RBAC, MFA |
| Code security | Find code flaws | SAST |
| Dependency security | Find vulnerable libraries | SCA |
| Dynamic testing | Test running apps | DAST |
| API security | Protect interfaces | API gateways, API security platforms |
| IaC security | Prevent misconfigurations | IaC scanners |
| Cloud posture | Detect cloud risk | CSPM |
| Workload protection | Secure runtime | CWPP |
| Unified cloud security | Correlate risk | CNAPP |
| Security operations | Detect and respond | SIEM, SOAR |
SAST, DAST, and SCA for Application Security
SAST audits source code for application flaws prior to deployment. DAST evaluates running applications from an external perspective to spot operational defects. SCA analyzes open-source dependencies and third-party packages for known vulnerabilities. Deploying these three tools together strengthens application security in cloud computing by giving defense teams complete coverage across code, dependencies, and application behavior.
CSPM, CWPP, and CNAPP for Cloud Security
CSPM tracks cloud configurations, compliance standards, and overall security posture. CWPP defends active workloads like containers and virtual machines throughout runtime. CNAPP connects cloud posture, workload telemetry, identity rights, and application security data into a single operational view.
IAM, API Security, and Secrets Management
IAM policies, part of broader cybersecurity measures, govern resource access for human users and automated services. RBAC rules and MFA enforce tight boundaries around privileged accounts and corporate identities. API security safeguards application interfaces using strict authentication, authorization policies, payload validation, and traffic management. Secrets management tools store API keys, tokens, certificates, and database credentials safely outside application source code.
SIEM, SOAR, and Runtime Threat Detection
SIEM systems aggregate security logs across applications, cloud platforms, and physical infrastructure. SOAR platforms trigger automated remediation actions based on incoming event data. Runtime detection monitors application processes and container activity to spot unauthorized privilege escalations and suspicious network connections.
Integrated Security Platforms vs Point Solutions
Point products deliver specialized capabilities for single tasks, but managing application security in cloud computing this way often leaves enterprise environments with redundant, overlapping tools. Tool proliferation generates duplicate alerts and fragmented findings across operations teams.
Choosing an integrated cybersecurity solution provider allows teams to combine application, identity, cloud, and runtime telemetry into unified management workflows. Security leaders must evaluate system compatibility with existing DevOps pipelines, coverage across development stages, threat prioritization methods, and long-term operational costs.
Severity scores alone cannot show which vulnerabilities can reach exposed applications, identities, workloads, or sensitive enterprise data.
Cloud Application Security Implementation for Enterprise Applications
Cloud application security implementation requires a structured operating model rather than isolated security tools. Enterprise programs align execution across seven stages: Assess → Prioritize → Architect → Integrate → Deploy → Monitor → Improve.
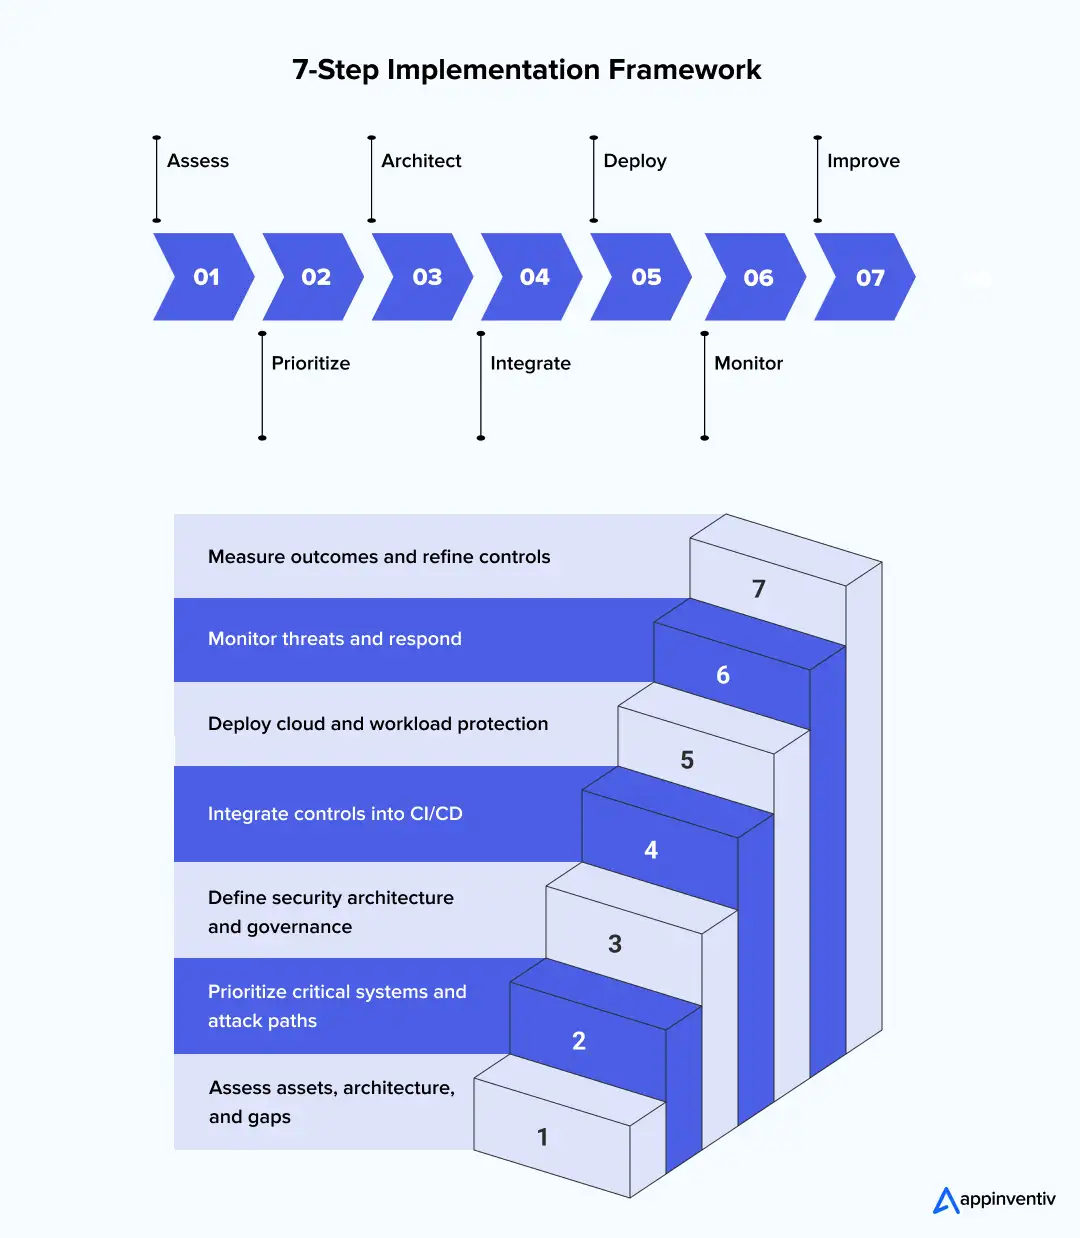
Step 1 – Assess Current Assets and Risk
Review system architecture, delivery workflows, regulatory demands, existing security controls, and known gaps. Security leaders evaluate system architecture, delivery workflows, regulatory demands, security gaps, and data integrity during migration where applicable.
Step 2 – Identify Critical Systems and Attack Paths
Operations teams rank applications by revenue impact, data sensitivity, public exposure, and risk. Security analysts map connections across identities, APIs, and cloud resources to expose pathways reaching core data.
Step 3 – Define Governance and Security Architecture
Security leaders establish baseline standards for IAM, encryption, API protection, secrets management, logging, and vulnerability remediation as part of a broader cybersecurity strategy implementation plan. Development managers assign clear ownership and approval workflows before teams launch new cloud services.
Step 4 – Integrate Security Into Delivery Pipelines
Automated build systems run static code analysis, dependency verification, secrets scanning, IaC testing, and container security inside CI/CD workflows. Deployment gates block high-risk code defects before release.
Step 5 – Deploy Cloud and Workload Controls
Deploy the required cloud, identity, API, container, and workload controls across production. Apply common policies across environments and assign findings to clear remediation owners.
Step 6 – Monitor Operations and Respond to Incidents
Centralized logging platforms aggregate telemetry across applications, cloud environments, identities, and active workloads. Response teams define clear containment steps for compromised credentials, vulnerable apps, and data leakage.
Step 7 – Measure Outcomes and Refine Controls
Security leaders track overdue vulnerabilities, mean remediation time, exposed assets, policy violations, and pre-deployment bug blocks to refine security controls.
Benefits of Cloud Application Security Solutions for Enterprises
The benefits of cloud application security solutions extend beyond breach prevention. A structured program reduces security risk, remediation effort, and operational complexity.
- Reduce Exposure to Application and Cloud Threats: Automated security scans detect vulnerable source code, exposed APIs, broad permissions, and misconfigured infrastructure before attackers exploit them.
- Protect Sensitive Enterprise and Customer Data: Strong encryption, access management, secrets isolation, and active telemetry defend financial records, customer details, and proprietary intellectual property.
- Accelerate Secure Application Releases: Automated security checks running inside build pipelines provide software engineers with fast feedback before production deployments. Automated rules handle routine code updates and reserve engineering attention for high-risk app changes.
- Improve Vulnerability Remediation: Risk-focused prioritization directs engineering resources toward app defects impacting public-facing systems. Technical teams spend less time investigating low-impact alerts and minor code flaws.
- Strengthen Compliance and Governance: Centralized access rules, audit logs, identity controls, and continuous scans satisfy regulatory requirements across cloud environments.
- Improve Cloud Visibility and Operational Control: Unified tracking across application code, APIs, user identities, workloads, and cloud settings reveals precise risk locations and assigned remediation owners.
- Reduce Security Operations Complexity: A consolidated approach to cloud-based application security eliminates duplicate findings generated by code scanners, cloud monitors, and workload defense. Defense teams analyze connected risk telemetry through consolidated management workflows.
- Protect Business Continuity and Customer Trust: Rapid threat detection and swift incident response minimize the impact of operational disruptions, data exposure, and security breaches. Clear security controls preserve corporate reputation and client trust in digital services.
Also Read: Unleashing the Potential of Cloud in Digital Transformation
Cloud Application Security Services for Enterprise Cloud Modernization
Enterprise cloud application security services align application development and cybersecurity within a single operating model.
Cloud-Native Application Development
Cloud-native development spans microservices, APIs, container registries, Kubernetes orchestrators, and cloud architectures. Security rules guide system designs from initial architecture phases rather than appending controls after code completion, an approach many teams support through DevOps outsourcing.
Cloud Migration and Modernization
Legacy applications require architectural adjustments prior to moving into cloud environments. Modernization services guide application re-architecture, containerization, workload migration, and multi-cloud deployments without compromising core security policies.
DevSecOps and Application Security Engineering
Automated controls integrate into build pipelines through static code analysis, app dependency audits, DAST scans, secrets scanning, and infrastructure checks. Early verification helps application teams identify and resolve code flaws before production releases.
Cloud Security Engineering
Cloud security operations govern identity policies, posture management, workload protection, network isolation, baseline configurations, and system monitoring. These controls safeguard underlying cloud resources supporting core software applications.
Also Read: Cloud Business Intelligence – How can the two technologies help your business grow?
API and Application Security
Interface protection enforces identity checks, authorization rules, payload validation, traffic management, and vulnerability scans. Real-time telemetry monitors application execution to flag suspicious behavior and active attack vectors.
Enterprise Security and Compliance
Large organizations require operational governance covering security policies, risk assessments, audit requirements, and regulatory mandates. Continuous monitoring tracks compliance postures and system modifications across cloud environments.
Cloud Application Security vs Traditional Application Security
Traditional application security protects applications running on infrastructure controlled by a single organization. Cloud applications depend on distributed services, shared infrastructure, APIs, and changing workloads. Effective cloud application security strategies must address these architectural differences directly.
| Area | Traditional Application Security | Cloud Application Security |
|---|---|---|
| Architecture | Centralized or monolithic | Distributed and cloud-native |
| Infrastructure | Organization-controlled | Shared responsibility |
| Identity | Perimeter-oriented | Identity-centric |
| Deployment | Periodic releases | Continuous deployment |
| APIs | Limited role | Central to application architecture |
| Dependencies | Smaller ecosystem | Extensive third-party dependencies |
| Runtime | Relatively stable | Transient and ephemeral |
| Visibility | Centralized oversight | Multi-cloud and distributed |
| Security | Periodic testing | Continuous security controls |
Emerging Trends Shaping Cloud Application Security
Enterprise cloud security moves away from isolated checks toward connected controls across development, cloud infrastructure, and runtime environments. Modern operational shifts alter how technical leaders design cloud application security programs and select platforms.
- Code-to-Cloud Risk Correlation: Security platforms link static code findings directly to active cloud resources running that application. Threat correlation identifies vulnerabilities creating reachable attack paths into critical systems.
- CNAPP Consolidation: Organizations consolidate redundant security tools by unifying cloud posture, workload telemetry, identity governance, and application protection. Unified platforms eliminate fragmented findings and give defense teams a single operational view.
- AI-Assisted Security Operations: Automated intelligence processes large volumes of security telemetry, correlates related events, and accelerates investigation workflows, a trend covered in depth in our piece on AI in cybersecurity. Practical outcomes depend on underlying application, identity, cloud, and runtime data quality.
- Identity-First Cloud Security: Cloud architectures depend heavily on user logins, service accounts, workload identities, and temporary tokens. Defense programs prioritize entitlement analysis, identity risk scoring, and strict least-privilege enforcement across human and service access.
- Automated Vulnerability Remediation: Security platforms progress beyond vulnerability discovery toward guided and automated remediation actions. Routine tasks include dependency upgrades, system configuration fixes, policy updates, and direct ticket creation inside developer tools.
- Runtime Application Protection: Pre-deployment testing cannot catch every exploit targeting live environments. Runtime controls monitor abnormal process activity, workload modifications, privilege abuse, and active attacks after code deployment.
- Software Supply Chain Security: Development teams audit open-source libraries, transitive dependencies, base container images, build pipelines, and app provenance. Supply chain verification integrates directly into standard application security routines.
- API and Non-Human Identity Security: Modern app architectures generate high volumes of API calls and machine-to-machine connections. Security teams expand monitoring beyond human users to cover service tokens, API permissions, credential usage, and abnormal inter-service communication.
Why Enterprises Need an Integrated Cloud and Cybersecurity Strategy
The importance of cloud application security is easy to underestimate until isolated organizational structures start to weaken it. Application developers manage source code, cloud engineering manages infrastructure, and security analysts manage threats, each playing a role outlined in our cloud computing guide for businesses. Operational governance and regulatory requirements demand continuous oversight across all three groups.
Disconnected teams require unified visibility and explicit task ownership. Source code defects must trace straight to impacted runtime workloads. Identity risks must map directly to accessible application resources and data assets.
An integrated strategy unifies cloud architecture, secure development, defense operations, continuous monitoring, and ongoing program improvement. Unified governance establishes consistent controls across development stages and eliminates operational gaps between application security teams. Clear risk context guides faster threat remediation across build pipelines and live production environments.
Re-architecting legacy applications without connecting cloud engineering and cybersecurity can introduce new exposure across APIs, workloads, identities, and data.
Build and Secure Cloud-Native Applications With Appinventiv
Appinventiv helps enterprise technology leaders build cloud-native apps and strengthen cloud application security across development, deployment, and runtime environments. Our technical teams combine cloud engineering with cybersecurity operations, connecting defensive controls directly to protected systems.
- Cloud-Native Application Architecture and Modernization: Engineers construct and modernize apps using microservices, APIs, container registries, Kubernetes clusters, and cloud platforms. Technical teams manage legacy migrations, application re-architecture, and multi-cloud deployments.
- Secure Development and DevSecOps: Automated security checks integrated into continuous delivery pipelines using SAST, SCA, DAST, secrets detection, and IaC scanning. Early scanning provides software developers with actionable feedback before dangerous updates reach production.
- Cloud and Application Security Engineering: Cybersecurity operations govern identity rights, access permissions, API protection, vulnerability testing, workload defenses, system configurations, event logging, and compliance reporting. Defense mechanisms protect application code throughout build phases and live runtime operations.
Appinventiv has completed 500+ cloud migrations, 2,000+ cloud services deployments, and 20+ hybrid-cloud environments across 35+ industries. Our practice maintains 50+ cloud specialists, 5 strategic cloud partnerships, and round-the-clock infrastructure monitoring. Client outcomes demonstrate up to 30% cloud spending cuts, 99.90% operational uptime, and double the infrastructure output.
Our development teams assist technology leaders in modernizing existing applications, addressing security gaps, or building new cloud-native products. Speak with our cloud engineering and cybersecurity specialists to review your application goals.
FAQs
Q. What are the main cloud application security issues?
A. Common issues include cloud misconfigurations, insecure APIs, excessive permissions, vulnerable dependencies, exposed secrets, container vulnerabilities, build weaknesses, and unmanaged cloud applications. Enterprise teams face operational friction from tool proliferation, fragmented policies, restricted visibility, and delayed vulnerability remediation.
Q. How do AI and automation impact cloud application security?
A. Automated tools analyze large volumes of telemetry, correlate related findings, detect abnormal process behavior, and accelerate threat remediation. Automated pipelines run security scans across delivery workflows, infrastructure settings, and running workloads. Machine intelligence provides security analysts with context and structured rules without replacing human review for critical decisions.
Q. What are the compliance challenges in cloud application security?
A. Enterprise organizations manage diverse regulatory demands across multiple countries, business divisions, and cloud environments. Primary obstacles include inconsistent access rules, incomplete audit logs, unmapped data stores, weak retention policies, and limited visibility into third-party services. Centralized policies, continuous monitoring, routine access reviews, and audit records help maintain regulatory compliance across applications.
Q. What features should a robust cloud application firewall include?
A. A cloud application firewall protects against common web attacks, interface abuse, malicious requests, and application-layer threats. Critical capabilities include custom security rules, managed threat signatures, bot detection, rate limiting, API protection, SSL inspection, traffic monitoring, and security logging. Enterprise environments require central policy controls and unified visibility across application fleets.
Q. How can companies implement cloud application security?
A. Operations teams inventory applications, APIs, cloud resources, dependencies, identities, and active workloads. Security analysts evaluate business-critical systems and map realistic attack pathways into core data. Engineering leaders establish security governance, embed SAST, SCA, secrets scanning, DAST, and IaC checks into build pipelines, and apply IAM, API, posture, and workload controls. Continuous monitoring, incident response routines, and regular security audits follow deployment.
Q. What technologies form a cloud application security stack?
A. Security architecture depends on application designs and cloud environments. Development security uses SAST, SCA, and DAST to test code and third-party dependencies. Platform protections combine IAM for access control, API gateways for interfaces, CSPM for cloud posture, and CWPP for workload execution. CNAPP platforms unify cloud risks, and SIEM tools manage detection and incident response. Technical leaders evaluate tool integration, pipeline coverage, automation, scalability, and operational overhead before selecting technology vendors.

Fast 2-minute response, fully NDA-protected.
How to Hire the Right Cybersecurity Expert for Your Business
Key Takeaways Define the business risk before choosing a security title or engagement model. Match the role to the environment, whether the priority is cloud, application, compliance, incident response, or network defense. Evaluate cybersecurity professionals through relevant scenarios, practical tasks, evidence, and references. Compare permanent, consulting, managed, and hybrid models against the coverage the business…
How to Prevent Social Engineering Attacks in the Enterprise: Types, Examples, and Defense Strategies
Key takeaways: Social engineering attacks exploit human trust, making even well-secured enterprises vulnerable to a single convincing interaction. AI is making phishing, vishing, and impersonation attacks faster to launch, harder to detect, and easier to scale. Strong verification processes are essential, especially for credential resets, financial requests, and other high-risk actions. Phishing-resistant authentication, least-privilege access,…
Cybersecurity Compliance Requirements Every Enterprise Needs in 2026
Key takeaways: Compliance is now a core business priority, influencing revenue, market access, and customer trust. Enterprises must navigate multiple overlapping regulations across industries and regions. Unified compliance controls help reduce duplicated work, complexity, and overall costs. Continuous monitoring and risk assessments help identify compliance gaps before they become costly issues. Automation streamlines evidence collection,…